Call Us Today! 877-659-2467

What are the Identified Risks in Healthcare Data Breaches?

Vendor Risk Is the New Front Line

Healthcare organizations continue to report substantial data breaches in 2026. Hacking and IT incidents dominate reports to the HHS Office for Civil Rights (OCR). Large breach reports have eased slightly compared with 2025. However, third-party vendors and business associates continue to concentrate risk across healthcare.

The Healthcare Breach Landscape

During the first half of 2026, organizations reported 397 large healthcare breaches to OCR. These incidents affected approximately 33.8 million individuals. Although those figures declined from the previous year’s first half, they still represent substantial exposure.

Business associates played a role in approximately 43% of large breach reports. Hacking and IT incidents accounted for most cases. Several incidents illustrate how vendors, applications, and shared technology can expose patient information.

Notable 2026 examples illustrate the pattern:

DentaQuest

A May 2026 cyber incident affected approximately 15 million individuals connected to DentaQuest, a Sun Life subsidiary. The ShinyHunters extortion group claimed responsibility for the incident. The compromised information included names, addresses, Social Security numbers, and Medicare or Medicaid identifiers. It also included dental or vision information, such as diagnoses, treatment details, and billing records. DentaQuest began notifying individuals in July after the group reportedly leaked data following failed negotiations.

iRhythm Technologies

A June 2026 incident affected approximately 8.18 million people connected to iRhythm Technologies. Attackers used social engineering to access business applications hosted by third parties. The incident did not involve clinical systems or medical devices. The exposed information included names, contact details, birth dates, insurance numbers, account identifiers, serial numbers, and service dates. The company began notifications in October. At that time, it reported no evidence of identity theft.

Blueberry Pediatrics

An incident involving Blueberry Pediatrics affected approximately 341,000 individuals, including children. Attackers exploited a vulnerability in Metabase, a business intelligence and reporting tool. A related incident involving prescription partner Photon stemmed from the same vulnerability. The exposed information included names, birth dates, health plan details, and certain medical and billing information. Blueberry Pediatrics discovered the incident in August 2026 and began notifications in October.

Earlier Breaches Continue to Create Financial Consequences

Conduent’s 2024–2025 breach affected approximately 62.2 million individuals. The incident recently prompted an $80 million class-action settlement agreement.

Change Healthcare’s 2024 ransomware attack remains the largest reported healthcare breach, affecting approximately 192.7 million individuals.

These incidents show how one organization’s security failures can affect patients and healthcare partners nationwide.

OCR Continues to Prioritize Risk Analysis

OCR continues its Risk Analysis Initiative. Recent settlements repeatedly identify failures to conduct accurate and thorough risk analyses under the HIPAA Security Rule. The requirement appears at 45 CFR § 164.308(a)(1)(ii)(A). Several 2026 settlements highlight these recurring weaknesses.

Ambry Genetics

Ambry Genetics agreed to a $700,000 settlement following a phishing incident affecting approximately 225,000 people. OCR also identified concerns involving access termination and unique user identifiers.

OSF HealthCare System

OSF HealthCare System agreed to a $552,250 settlement involving a ransomware incident affecting approximately 54,000 individuals. OCR identified failures involving risk analysis, impermissible disclosures, and breach notification.

Spencer Gifts LLC

Spencer Gifts LLC agreed to a $450,000 settlement involving its employer-sponsored health plan after a ransomware attack. The case demonstrates that HIPAA obligations can extend beyond traditional healthcare providers.

Patient Access Still Drives Enforcement

OCR also continues its Right of Access Initiative. Shen Smiles, a Pennsylvania dental practice, agreed to a $140,000 settlement involving delayed patient access to records. OCR also identified related Privacy Rule deficiencies. The case reinforces a critical point: organizations can face HIPAA enforcement without experiencing a cyberattack.

What These Cases Mean for Healthcare Organizations

Vendor oversight requires ongoing attention.

Business associates, cloud applications, reporting tools, and billing partners create additional opportunities for unauthorized access. Identify which vendors create, receive, maintain, or transmit protected health information. Evaluate their safeguards and document your oversight. Address your organization’s HIPAA responsibilities when vendors handle patient information.

Risk analysis must reflect actual operations

An incomplete or outdated assessment can overlook significant threats. Include third-party applications, connected devices, remote access, and every location that stores or processes electronic protected health information. Evaluate phishing, social engineering, ransomware, and vendor vulnerabilities. Document identified risks, assign responsibility, and track corrective actions.

Contracts and notification procedures need clear ownership

Business associate agreements should clearly define incident reporting duties and applicable responsibilities. Organizations must also understand their own patient and OCR notification obligations. Practice your response before an incident forces urgent decisions.

Financial consequences extend beyond regulatory settlements

Breaches can trigger class action lawsuits, state investigations, operational disruptions, and substantial recovery expenses. Organizations may also pay for forensic investigations, notifications, monitoring, and system restoration. Patient trust can take much longer to rebuild.

Five Actions to Take Now

  1. Update your risk analysis. Include third-party systems, current threats, and changes in your operations.
  2. Review high-risk vendors. Request meaningful evidence of security controls and evaluate how those safeguards protect your information.
  3. Test your incident response procedures. Confirm reporting contacts, notification timelines, decision responsibilities, and procedures for vendor incidents.
  4. Strengthen patient access procedures. Train staff to recognize requests, track deadlines, document responses, and escalate delays.
  5. Review cyber insurance. Examine coverage limits, vendor-related incidents, exclusions, and policy conditions with your insurance professional.

Attackers exploit weaknesses throughout the healthcare ecosystem. OCR continues to evaluate organizations against core HIPAA requirements.

Organizations that treat risk analysis, vendor management, and incident response as continuous disciplines, not annual checkboxes, will be better positioned as these trends evolve.

This article is for informational purposes only and does not constitute legal advice. Organizations should consult qualified counsel regarding specific compliance obligations.

When was the last time your organization updated its HIPAA security risk analysis?

Aris Medical Solutions can help you identify compliance gaps and prevent costly data breaches.
Schedule your HIPAA compliance review today and protect your organization from the next enforcement headline.

Your Trusted Partner for HIPAA Compliance since 2009
Is Your Medical Practice Prepared for the Cybersecurity Threats that are Increasing?

New cybersecurity statistics reveal why healthcare organizations must strengthen their security safeguards.

Cybercriminals continue to target healthcare organizations, regardless of their size. Small medical practices, dental offices, and business associates face many of the same threats as larger healthcare systems.

The 2026 Verizon Data Breach Investigations Report highlights growing cybersecurity risks and the importance of basic security safeguards. The report analyzed more than 31,000 security incidents and 22,000 confirmed data breaches worldwide. These findings demonstrate why healthcare organizations must take cybersecurity seriously.

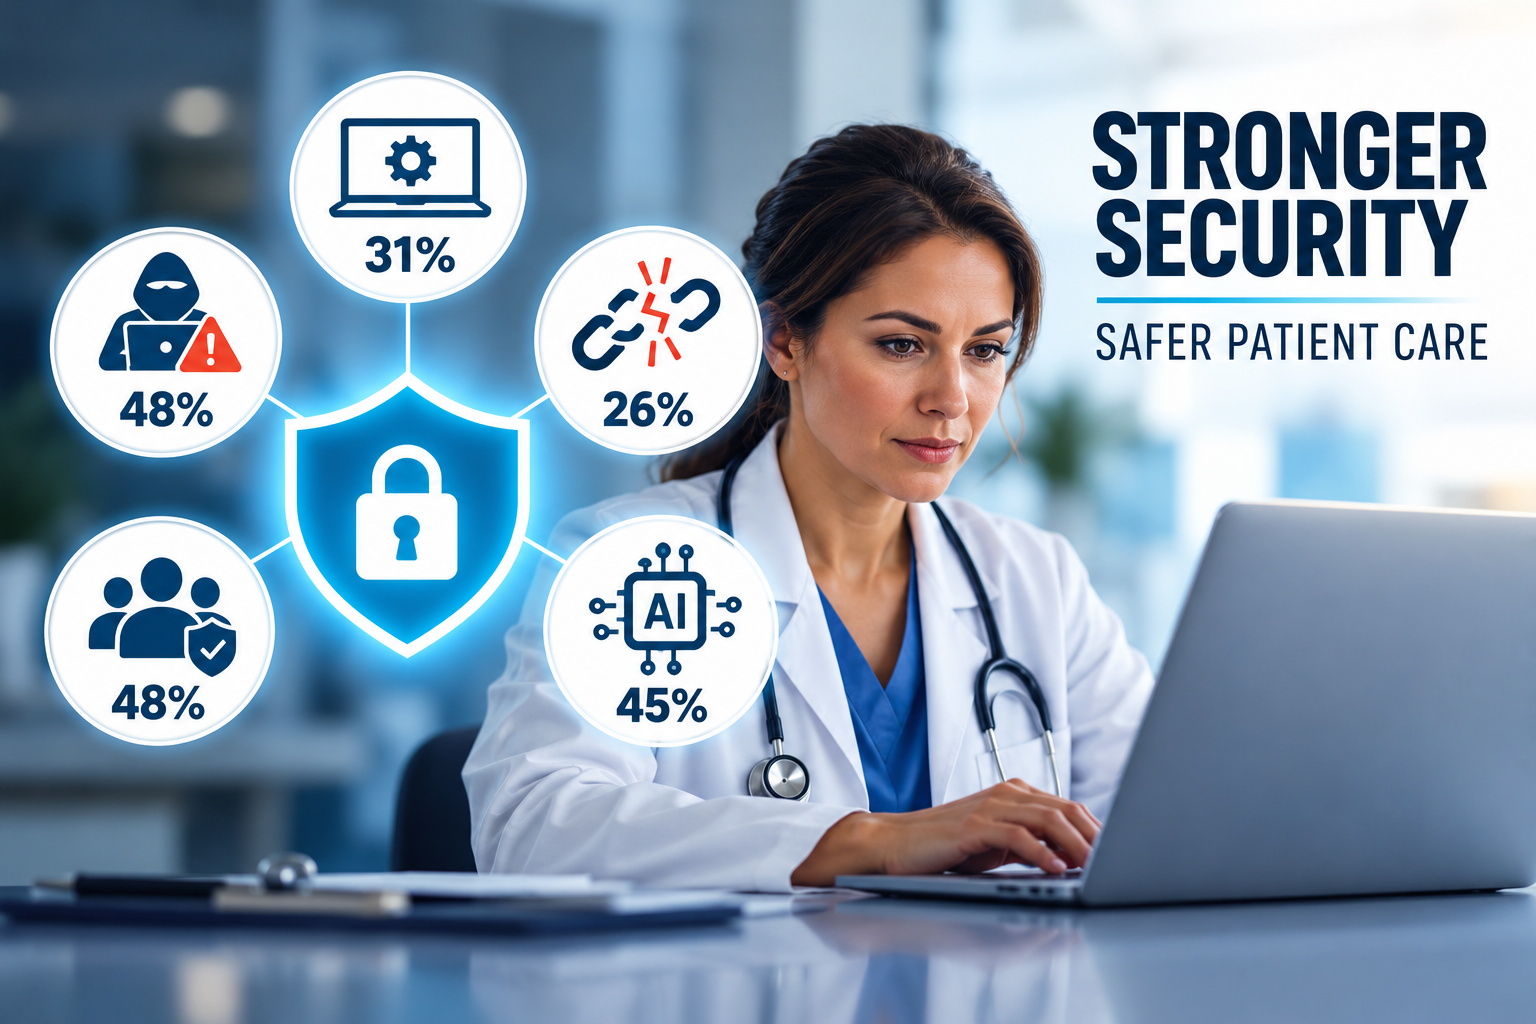
31% of Data Breaches Begin with Exploited Vulnerabilities

Cybercriminals frequently exploit weaknesses in software, networks, and security configurations. Verizon reports that vulnerability exploitation accounted for 31% of breaches in its 2026 analysis. This finding reinforces the importance of identifying and correcting security weaknesses before attackers exploit them. Healthcare organizations should conduct regular vulnerability assessments, install security patches, and review system configurations. However, vulnerability assessments alone do not satisfy HIPAA’s Security Risk Analysis requirements. Organizations must evaluate threats, vulnerabilities, existing safeguards, and potential risks to patient information. A comprehensive HIPAA Security Risk Analysis helps organizations identify risks to electronic Protected Health Information (ePHI).

48% of Data Breaches Involve Ransomware

Ransomware remains one of the most serious cybersecurity threats facing healthcare organizations. Verizon found ransomware involvement in 48% of confirmed breaches analyzed in its 2026 report. These attacks can encrypt medical records, interrupt patient care, and disrupt daily operations. Healthcare organizations must prepare for more than restoring computer systems. They need documented contingency plans that address emergency operations, data recovery, and system restoration. Regular backups, recovery testing, and employee training help organizations prepare for ransomware attacks. A disaster recovery plan should identify critical systems, recovery priorities, and responsible personnel. A written plan provides little protection unless the organization tests it and maintains it.

Only 26% of Known Exploited Vulnerabilities Were Fully Remediated

Identifying security weaknesses represents only the first step toward protecting patient information. Verizon reported that organizations fully remediated only 26% of tracked, known exploited vulnerabilities during 2025. The median time to resolve these vulnerabilities increased from 32 days to 43 days. These findings highlight a dangerous gap between identifying security risks and correcting them. Medical practices should maintain documented procedures for identifying, prioritizing, and correcting security vulnerabilities.

A Risk Management Plan helps organizations assign responsibilities, establish deadlines, and track corrective actions. HIPAA compliance requires organizations to address identified risks, not simply document their existence.

48% of Data Breaches Involve Third Parties

Healthcare organizations depend on outside vendors to manage technology, billing, records, and other essential services. Unfortunately, these relationships can introduce additional cybersecurity risks. Verizon found that third parties played a role in 48% of breaches analyzed in its 2026 report. Third-party breach involvement also increased significantly compared with the previous reporting period. Medical practices should evaluate the security practices of vendors that access, process, or store patient information.

A signed Business Associate Agreement establishes important legal responsibilities, but it does not guarantee adequate cybersecurity protection. Organizations should review vendor safeguards, incident reporting procedures, access controls, and subcontractor relationships. Regular vendor oversight helps identify weaknesses before they expose patient information.

Artificial Intelligence Creates New Security Challenges

Artificial intelligence offers healthcare organizations opportunities to improve efficiency and streamline administrative tasks. However, unauthorized AI tools can introduce significant privacy and security risks. Verizon reported that regular employee AI use on corporate devices increased from 15% to 45%. This figure includes authorized and unauthorized AI use. The report also identified unauthorized AI activity as a growing source of potential data exposure. Employees may unknowingly expose confidential information by entering sensitive data into unapproved AI applications. Healthcare organizations should establish clear AI policies and train employees on acceptable use. They should also evaluate AI vendors before allowing access to patient information. When applicable, organizations must obtain Business Associate Agreements and implement appropriate safeguards.

Basic Cybersecurity Safeguards Make a Difference

Healthcare organizations do not need to wait for a cyberattack to strengthen their defenses. They can reduce cybersecurity risks by implementing and maintaining essential safeguards.

These safeguards include:

  • Conducting comprehensive Security Risk Analyses.
  • Developing and updating Risk Management Plans.
  • Maintaining an asset list and include how data flows through your network.
  • Performing vulnerability assessments and applying security patches.
  • Implementing multifactor authentication and appropriate encryption.
  • Maintaining secure system configurations and access controls.
  • Training employees to recognize phishing and other cyber threats.
  • Reviewing Business Associate and vendor security practices.
  • Developing and testing contingency and disaster recovery plans.
  • Monitoring system activity and investigating suspicious behavior.
  • Establishing policies for artificial intelligence and sensitive information.

These actions help organizations protect patient information and maintain essential healthcare operations.

HIPAA Compliance Is More Than Checking a Box

Many healthcare organizations mistakenly believe that purchasing cybersecurity software satisfies their HIPAA obligations. However, technology represents only one component of an effective HIPAA compliance program. Organizations must also establish policies, train employees, evaluate risks, and document corrective actions.

A comprehensive compliance program combines administrative, physical, and technical safeguards. The HIPAA Security Rule requires covered entities and business associates to protect electronic patient information. These requirements apply regardless of an organization’s size.

Small practices cannot assume that cybercriminals will overlook them.

The Bottom Line: Prevention Costs Less Than Recovery

A cybersecurity incident can create significant financial, operational, and reputational consequences. Medical practices may face business interruptions, recovery expenses, regulatory investigations, and damaged patient trust.

Although no security program can eliminate every threat, proactive safeguards can significantly reduce risks. Healthcare organizations should focus on preventing incidents while preparing to respond when something goes wrong.

Protecting patient information is not a one-time project. It requires continuous attention, documented safeguards, and ongoing risk management.

The question is not whether your organization can afford cybersecurity.

The question is whether your organization can afford the consequences of inadequate protection.

When was the last time your organization updated its HIPAA security risk analysis?

At Aris Medical Solutions, our HIPAA Keeper™ cloud-based platform makes HIPAA compliance simple. It guides your organization through every requirement with a clear, step-by-step process. From risk analyses, risk management, policies to employee training and required documentation, you’ll have everything needed to remain compliant, protected, and audit-ready. Best of all, your HIPAA Compliance Officer is never on their own. Every client has access to a Certified HIPAA Security Analyst who provides expert guidance, answers questions, and helps ensure your compliance program is implemented correctly.

Schedule your HIPAA compliance review today and protect your organization from the next enforcement headline.

Your Trusted Partner for HIPAA Compliance since 2009
Sources

  1. Verizon, 2026 Data Breach Investigations Report.
  2. Verizon, 2026 DBIR Healthcare Industry Snapshot.
  3. Center for Internet Security, CIS Controls and MS-ISAC Insights Featured in Verizon’s 2026 Data Breach Investigations Report.

Note: The reported percentages reflect different datasets and measures. They do not represent breach rates for all medical practices.

Phishing Prevention for Healthcare

Healthcare is one of the most targeted industries for phishing because attackers know the environment is fast-paced, staff are busy, and ePHI is extremely valuable. All it takes is one click on a malicious email to shut down your systems, expose patient data, and put your practice in OCR’s crosshairs.

Phishing is behind most ransomware incidents reported to OCR, and many recent enforcement actions stemmed from preventable, basic phishing mistakes. With proper training, employees can stop the majority of Security Rule violations before they happen.

Below is the top phishing tactics used against medical and dental practices, followed by practical prevention steps aligned with HIPAA Compliance and Security Rule requirements.

1. Email Spoofing & Look-Alike Domains

What it looks like

  • Fake emails appear to come from a doctor, CEO, billing manager, or IT vendor.
  • Domains slightly change (e.g., mayoclinic.com vs mayoclinic.net).
  • “Urgent request” messages: invoice approvals, password resets, or wire transfer requests.

Why it works

Healthcare staff often trust internal names and don’t closely examine sender details.

How to prevent it

  • Enable DMARC, DKIM, and SPF on your email domain.
  • Require multi-factor authentication (MFA) for all email access.
  • Train staff to hover over the sender address before opening attachments.
  • Implement Role-Based Access Controls so fewer people can approve financial or patient-record changes.

2. Malicious Attachments (PDF, Fax, Lab Result, eRx Notice)

What it looks like

  • “Incoming fax” from eFax, RingCentral, or RightFax
  • “New lab results attached”
  • “Updated referral forms – review immediately”

Attachments often contain ransomware droppers or credential-stealing malware.

Why it works

Clinicians and staff open attachments quickly due to workflow pressure.

How to prevent it

  • Deploy email sandboxing (advanced email scanning).
  • Block macros and executable files.
  • Require staff to verify unexpected clinical attachments by calling the sender directly.
  • Maintain current endpoint detection & response (EDR) software.

3. Credential Harvesting / Fake Login Pages

What it looks like

  • Fake Microsoft 365, Google Workspace, EHR, or billing portal login prompts.
  • Emails claim “Your mailbox is full—log in to restore access,” or “Your password needs to be reset.”

Why it works

Providers often keep multiple portals open and may not notice small differences.

How to prevent it

  • Enforce MFA, which stops most credential-theft logins.
  • Train employees not to click on the links within the email.
  • Train employees to check the URL before entering credentials.
  • Use password managers that auto-fill only on real sites.

4. Vendor Impersonation (EHR, Imaging, Billing, Clearinghouses)

What it looks like

  • Fake messages from Athena, eClinicalWorks, Change Healthcare, Kareo, etc.
  • “Urgent update required to prevent claim rejections.”
  • “Your portal access will be disabled unless you verify your account.”

Why it works

Healthcare providers rely heavily on third-party systems and trust vendor branding.

How to prevent it

  • Verify updates by logging in directly and never through email links.
  • Maintain a Vendor Verification Checklist under your HIPAA Security Rule documentation.
  • Require IT department to approve all vendor-related system changes.

5. Business Email Compromise (BEC)

What it looks like

  • A hacked internal account sends messages to other employees.
  • Requests for W-2s, bank changes, ACH updates, or large transfers.
  • Email rules silently forwarding messages to attackers.

Why it works

It comes from a real account and staff trust it.

How to prevent it

  • Require MFA on all accounts.
  • Set alerts for email forwarding rule creation.
  • Use conditional access and login-location alerts.
  • Review account audit logs regularly.

6. “Patient Refund” or “Billing Issue” Scams

What it looks like

  • Fake patient messages: “I was overcharged, please open the attached statement.”
  • Calls followed by phishing emails requesting account verification.

Why it works

Front-desk and billing teams want to resolve patient issues quickly.

How to prevent it

  • Never open unknown attachments claiming to be patient documentation.
  • Require all inbound patient documents to be sent via HIPAA-secure channels only.
  • Train non-clinical staff (front desk, billing, schedulers) since they are the most targeted.

7. Ransomware Delivery via Phishing

What it looks like

  • Fake faxes, statements, or shipping notifications.
  • Attachments disguised as scanned documents.

Why it works

One click can deploy ransomware that halts clinical operations.

How to prevent it

  • Maintain image-based backups (not just data backups).
  • Test your Contingency Disaster Recovery & Emergency Mode Operations Plan quarterly.
  • Ensure all devices are patched and running updated security tools.

8. Social Engineering Phone + Email Combination (“Hybrid Attacks”)

What it looks like

  • A phone call claiming to be from IT followed by an email link.
  • Attackers pretending to be from a lab, insurer, or specialist office.

Why it works

Healthcare workflow relies on phone + fax + email and attackers exploit the mix.

How to prevent it

  • Create a verification protocol for anyone asking for access or information.
  • Maintain a list of trusted numbers for labs, hospitals, and vendors.
  • Train staff never to act on unsolicited “IT support” messages.

Protect Your Organization Before It’s Too Late

HIPAA compliance isn’t a one-time project — it’s an ongoing process. At Aris Medical Solutions, our HIPAA Keeper™ system simplifies compliance with a cloud-based platform that walks you through each requirement, step by step. From risk analysis to training and documentation, you’ll have everything you need to stay protected, compliant, and audit ready.

Protect your practice — and your patients.


Schedule a free HIPAA checkup today at Aris Medical Solutions. Your HIPAA Compliance Officer will have a HIPAA security analyst to guide and assist them every step of the way.

HIPAA Settlement of $25K with New York Neurology Practice Over Ransomware Attack

The U.S. Department of Health and Human Services Office for Civil Rights (OCR) has reached a settlement with Comprehensive Neurology, a small neurology practice based in New York, following a potential violation of the HIPAA Security Rule. The investigation stemmed from a ransomware attack that compromised the electronic protected health information (ePHI) of patients.

OCR’s investigation revealed potential failures by the practice to implement adequate security measures required under the HIPAA Security Rule, such as conducting a thorough risk analysis and maintaining appropriate safeguards to protect ePHI. The breach impacted sensitive health data and underscored vulnerabilities in the practice’s cybersecurity defenses.

Ransomware and hacking remain the leading cyber threats to electronic health information in the healthcare sector. Ransomware, a form of malicious software (malware), is designed to block access to a user’s data—typically by encrypting it—until a ransom is paid. This settlement represents the 12th enforcement action related to ransomware and the 8th action under OCR’s ongoing Risk Analysis Initiative.

As part of the settlement, Comprehensive Neurology agreed to pay a monetary fine of $25K and implement a corrective action plan that will be monitored for two years to strengthen its HIPAA compliance program, including risk assessments, updated security policies, and staff training.

This case highlights the importance of proactive cybersecurity measures for all healthcare providers, regardless of size, and reinforces OCR’s commitment to protecting patient data in the face of increasing cyber threats like ransomware.

If you need assistance with HIPAA Compliance, check out our HIPAA Keeper™. Our online compliance system has everything you need to get compliant and stay compliant. Your HIPAA Compliance Officer will have a HIPAA security analyst to guide and assist them every step of the way!

For more information or to speak to someone about HIPAA Compliance call us at 877.659.2467 or use the contact us form.

Ransomware is a REAL threat…

By: Aris Medical Solutions

HIPAA Ransomware arismedicalsolutions.com

We all hope that we do not fall victim to ransomware, but we need to do more than just hope. All businesses, especially healthcare must have a contingency plan that includes data recovery in the event their systems are encrypted. If you have a backup that is NOT connected to your network, your downtime will be minimal. Keep in mind, you may need to go through the breach notification process based on your state and federal HIPAA law.

A Michigan ENT and Hearing practice refused to pay $6,500 in ransom and the hackers wiped their systems. With no chance of recovering this data, they chose to close the practice.
Most recently, a California Medical Practice was unable to recover their data after ransomware encrypted their systems including their backups. As a result, they will close their practice December 17, 2019.
I could keep adding to the list, but I would rather educate you on how to avoid this!

Best practice is of course to PREVENT ransomware in the first place. This starts with a solid network security program and education for your workforce. Most malware is introduced by an unsuspecting employee. Truly, one click of a mouse can cause a tumbling effect leading to the loss of your business. I know that sounds a bit dramatic, but most small to medium sized organizations that suffer a data breach do not survive.

Healthcare is a major target, in fact, 71% of ransomware attacks are towards small to medium sized practices since they do not have adequate network security in place.

  1. Your first line of defense is an enterprise version firewall device. This means, do not purchase one that has parental controls!
  2. Second, have a network security specialist set up your firewall and set custom security controls. It is fairly simple to set up a “network”, but it takes someone who truly understands network security to secure your network. This includes computers, servers, access points, etc.
  3. Depending on the size of your organization, you may need to set up an onsite server as a domain controller. Once this is in place, all users are authenticated through the domain. Security permissions can be set all at once and can’t be changed by the users.
  4. Phishing education for all employees including providers, and management. Business email addresses are targeted typically between Tuesday and Thursday according to the analysis from Barracuda. Phishing emails impersonate a trusted entity, they try to get the recipients to click on the links or attachments, share account credentials, and typically have some sort of urgency associated with the email. These emails often bypass traditional email security since they originate from reputable senders.
  5. Ensuring you have business associate agreements in place before releasing any PHI. This will protect you from fines and penalties in the event they have a data breach. It is advisable to carry cyber-liability insurance. If your business associate causes a data breach, it will still be your responsibility to go through the breach notification process. Best practice is to require your business associate to carry cyber liability as well.
  6. Physical security is often overlooked when we talk about data security. Portable devices need to be secured when left unattended. Printers and fax machines should not be located where they can be accessed by an unauthorized person. Servers should be in a locked room or cabinet. Computers should not be located near exits. Keeping an up to date inventory list and reviewing it regularly is critical in knowing if anything is missing. Lastly, a security system that has cameras and access logs is recommended.
  7. Organizations that have well defined policies and procedures are less likely to have a data breach. Employees are educated on what they can and cannot do with business equipment. Knowing what to do in the event of a security incident can actually STOP a data breach from becoming a major breach. Plus, most large fines are because the organization did NOT have a policy or plan in place. Just make sure you have read and dated them!

Remember HIPAA is not a once and done process, as technology changes and employees come and go, you need to keep track and update accordingly. Use your Risk Management Plan to track your progress! Let us know if you need any help with implementation.

If you would like more information, contact us at 877.659.2467 or complete the contact us form.

“Simplifying HIPAA through Partnership, Education, and Support”

How to protect yourself from Ransomware


By Aris Medical Solutions


This is actually easier said than done. However, there are some simple tips you can use to help guard yourself against this cyber warfare.

First of all let’s discuss what is Ransomware and why are these criminals doing this?
Ransomware is when an invader takes over your computer and encrypts your data and will not release it until you pay a “ransom”. Simply put, they do this to make money and, since it is a lucrative business, we do not see it going away anytime soon. With healthcare being such a popular target, you must be vigilant at all times.

Next, there are malicious malware and viruses that are used just want to be mean. Although I am not a fan of bumper stickers, I do like the one that says “Mean People Suck”. These criminals are the meanest of the mean. They don’t even give you the opportunity to pay a ransom. They just encrypt your data or delete it. I could go on and on explaining how all of this works, but instead let’s just talk about how to prevent this from happening in the first place!

Rule #1
Read the email carefully. More than likely you can spot misspelled words or subtle clues that the email is not authentic. Look closely at the email address. At a quick glance it may look like a legitimate email address. It will start with a prefix other than the original address and may even include a period (.) in a separate place. I have said this many times…rather than clicking on links or attachments in your email, open your browser and go to that particular website instead.

Rule #2
Again, do not EVER click on an attachment in an email that claims to have important information that you must act on immediately. For example:

  1. FedEx (UPS, USPS) was not able to deliver your package
  2. Your friend liked your post on Facebook, click to read more (some of these are true but it is best to open your browser and go to Facebook)
  3. A message about your credit card or bank account.
    There are many variations to these emails. Just exercise caution when opening your mail even from people you know. Their email account may have been hacked and being used to distribute the virus.

Rule #3
Keep a backup of any and all data that you want or need. Once the backup is created, disconnect it from your computer or network. If your system is ever violated, your backup will not be affected. Then you can wipe your system clean and restore your data.

Having a good anti-virus and anti-malware installed on your system are a necessity today, but it still only takes one click of a mouse to bring your network down because the software developers have to identify the problem before they can send out an update. Criminals are creating hundreds if not thousands of new viruses daily! Continual education for you and your staff is a must!

For more information on how Aris Medical Solutions can help your organization with HIPAA Compliance and Protecting your Practice call 877.659.2467 or click here to contact us.

“Protecting Organizations through Partnership, Education, and Support”

Patient Data is a Hot Commodity


By Aris Medical Solutions


Health care organizations are now a primary target since they are the custodians of patient data and a plethora of information. The reason patient information is sought after so much is because it can be sold on the black market for a decent price. Social Security Numbers also have a longer shelf life unlike credit card numbers. Therefore it is imperative that any company or person that is involved with healthcare data do what they can to protect their computers and/or network.

Criminals are diligent in trying to gain access to these valuable databases. They can get into your network through social engineering, malware, and mobile devices to name a few. Sadly, most attacks go undetected for months, sometimes even a year unless it is ransomware when you are “notified” immediately!

Under the Security Rule, all entities that work with Protected Health Information are required to conduct a Risk Analysis to uncover any potential vulnerabilities. Then they must create a Risk Management plan to correct those deficiencies. Although most of the “technical” standards are addressable and not required, this does not mean optional. All covered entities and business associates must have reasonable and appropriate safeguards in place to protect their data. Aside from your normal IT services, we believe it will only be a matter of time before network security audits will become mandatory. Keep in mind your Policies and Procedures are still the backbone of HIPAA Compliance.

So what can you do to protect your data and your organization?

  1. Conduct a security risk analysis
  2. Mitigate the vulnerabilities that are discovered
  3. Request a third party network security audit
  4. Request documentation that your business associates are HIPAA Compliant
  5. Continual EDUCATION!

These are just some of the basics that you should implement. For more information on how Aris Medical Solutions can help your organization with HIPAA Compliance and Protecting your Data call 877.659.2467 or click here to contact us.

“Protecting Organizations through Partnership, Education, and Support”

Healthcare is a huge target!


By Aris Medical Solutions


Things may seem wonderful since a new year is beginning; please don’t forget that many things remain the same.

For instance…
Healthcare is targeted in many ways. Do your employees know how to spot a phishing email or a potential virus? Most phishing expeditions and viruses are delivered right to your inbox! Did you know that nearly 90% of all ransomware attacks were on healthcare? A new report by Check Point software’s researchers states that Ransomware plague earns $2 million, while only 0.3% victims pay up. With this much money that is being made, more and more criminals are creating Ransomware. What would you do if one of your employees clicked on a link and downloaded a virus or your system was encrypted by ransomware?

Today, we are extremely busy and the criminals know this. It is so easy to spoof another company’s logo and create a phishing email or worse; a ransomware infection. What can you do? First and foremost you must continually educate your staff on what to look for and how to avoid making costly mistakes.

Here are some things to watch out for:

  1. Emails that claim your account has been compromised and you need to call a toll free number immediately. Lookup the number for the company and call them on that number and not the number supplied in the email. If you call the number that is supplied, either you will to talk to a real criminal and they try to get information from you or your credit card number. The other way is you get stuck in a voicemail holding pattern and then your number is programmed in and they call you back and try the same scam.
  2. Emails that claim your package (FEDEx / UPS / USPS) or payment (IRS / Bank / Credit Card) was not delivered, and you need to click on an attachment or a link.Open your browser and go directly to the company’s website, do not click on anything in the email.
  3. Phone call that advises you there is new software upgrade or virus and offers a free scan on your computer. Do not permit anyone access to your computer unless they have been verified by the company they work for and you know who they are.
  4. Fake apps that look like the real stores. Watch for apps that do not have a lot of reviews or bad reviews. Do not click on a link to download an app, go to the app store. Even then be careful, although Apple and Google use algorithms to detect, some have slipped through! Do not give out too much information and try to avoid adding any credit card numbers to apps. Read the permissions on all apps before downloading. If it is asking for more than is needed, do not download even though it sounds like a great app. Many apps contain malware to steal your information. If you connect your portable device to your office network, it can steal information from there as well.

Remember, most scams have a sense of urgency to prevent a negative consequence. Also, as the old saying goes… if it sounds too good to be true, it probably is. Always think before you react!
For more information on how Aris Medical Solutions can help your organization with HIPAA Compliance and Protecting your Data call 877.659.2467 or click here to contact us.

“Protecting Organizations through Partnership, Education, and Support”

©2026 Aris Medical Solutions – HIPAA Risk Management | HIPAA Compliance Consultants | All Rights Reserved | Terms and Conditions | Privacy Policy
The content and images on this website is owned by Aris Medical Solutions and their owners. Do not copy any content or images without our consent.
Powered by Bandwise LLC