Call Us Today! 877-659-2467

What are the Identified Risks in Healthcare Data Breaches?

Vendor Risk Is the New Front Line

Healthcare organizations continue to report substantial data breaches in 2026. Hacking and IT incidents dominate reports to the HHS Office for Civil Rights (OCR). Large breach reports have eased slightly compared with 2025. However, third-party vendors and business associates continue to concentrate risk across healthcare.

The Healthcare Breach Landscape

During the first half of 2026, organizations reported 397 large healthcare breaches to OCR. These incidents affected approximately 33.8 million individuals. Although those figures declined from the previous year’s first half, they still represent substantial exposure.

Business associates played a role in approximately 43% of large breach reports. Hacking and IT incidents accounted for most cases. Several incidents illustrate how vendors, applications, and shared technology can expose patient information.

Notable 2026 examples illustrate the pattern:

DentaQuest

A May 2026 cyber incident affected approximately 15 million individuals connected to DentaQuest, a Sun Life subsidiary. The ShinyHunters extortion group claimed responsibility for the incident. The compromised information included names, addresses, Social Security numbers, and Medicare or Medicaid identifiers. It also included dental or vision information, such as diagnoses, treatment details, and billing records. DentaQuest began notifying individuals in July after the group reportedly leaked data following failed negotiations.

iRhythm Technologies

A June 2026 incident affected approximately 8.18 million people connected to iRhythm Technologies. Attackers used social engineering to access business applications hosted by third parties. The incident did not involve clinical systems or medical devices. The exposed information included names, contact details, birth dates, insurance numbers, account identifiers, serial numbers, and service dates. The company began notifications in October. At that time, it reported no evidence of identity theft.

Blueberry Pediatrics

An incident involving Blueberry Pediatrics affected approximately 341,000 individuals, including children. Attackers exploited a vulnerability in Metabase, a business intelligence and reporting tool. A related incident involving prescription partner Photon stemmed from the same vulnerability. The exposed information included names, birth dates, health plan details, and certain medical and billing information. Blueberry Pediatrics discovered the incident in August 2026 and began notifications in October.

Earlier Breaches Continue to Create Financial Consequences

Conduent’s 2024–2025 breach affected approximately 62.2 million individuals. The incident recently prompted an $80 million class-action settlement agreement.

Change Healthcare’s 2024 ransomware attack remains the largest reported healthcare breach, affecting approximately 192.7 million individuals.

These incidents show how one organization’s security failures can affect patients and healthcare partners nationwide.

OCR Continues to Prioritize Risk Analysis

OCR continues its Risk Analysis Initiative. Recent settlements repeatedly identify failures to conduct accurate and thorough risk analyses under the HIPAA Security Rule. The requirement appears at 45 CFR § 164.308(a)(1)(ii)(A). Several 2026 settlements highlight these recurring weaknesses.

Ambry Genetics

Ambry Genetics agreed to a $700,000 settlement following a phishing incident affecting approximately 225,000 people. OCR also identified concerns involving access termination and unique user identifiers.

OSF HealthCare System

OSF HealthCare System agreed to a $552,250 settlement involving a ransomware incident affecting approximately 54,000 individuals. OCR identified failures involving risk analysis, impermissible disclosures, and breach notification.

Spencer Gifts LLC

Spencer Gifts LLC agreed to a $450,000 settlement involving its employer-sponsored health plan after a ransomware attack. The case demonstrates that HIPAA obligations can extend beyond traditional healthcare providers.

Patient Access Still Drives Enforcement

OCR also continues its Right of Access Initiative. Shen Smiles, a Pennsylvania dental practice, agreed to a $140,000 settlement involving delayed patient access to records. OCR also identified related Privacy Rule deficiencies. The case reinforces a critical point: organizations can face HIPAA enforcement without experiencing a cyberattack.

What These Cases Mean for Healthcare Organizations

Vendor oversight requires ongoing attention.

Business associates, cloud applications, reporting tools, and billing partners create additional opportunities for unauthorized access. Identify which vendors create, receive, maintain, or transmit protected health information. Evaluate their safeguards and document your oversight. Address your organization’s HIPAA responsibilities when vendors handle patient information.

Risk analysis must reflect actual operations

An incomplete or outdated assessment can overlook significant threats. Include third-party applications, connected devices, remote access, and every location that stores or processes electronic protected health information. Evaluate phishing, social engineering, ransomware, and vendor vulnerabilities. Document identified risks, assign responsibility, and track corrective actions.

Contracts and notification procedures need clear ownership

Business associate agreements should clearly define incident reporting duties and applicable responsibilities. Organizations must also understand their own patient and OCR notification obligations. Practice your response before an incident forces urgent decisions.

Financial consequences extend beyond regulatory settlements

Breaches can trigger class action lawsuits, state investigations, operational disruptions, and substantial recovery expenses. Organizations may also pay for forensic investigations, notifications, monitoring, and system restoration. Patient trust can take much longer to rebuild.

Five Actions to Take Now

  1. Update your risk analysis. Include third-party systems, current threats, and changes in your operations.
  2. Review high-risk vendors. Request meaningful evidence of security controls and evaluate how those safeguards protect your information.
  3. Test your incident response procedures. Confirm reporting contacts, notification timelines, decision responsibilities, and procedures for vendor incidents.
  4. Strengthen patient access procedures. Train staff to recognize requests, track deadlines, document responses, and escalate delays.
  5. Review cyber insurance. Examine coverage limits, vendor-related incidents, exclusions, and policy conditions with your insurance professional.

Attackers exploit weaknesses throughout the healthcare ecosystem. OCR continues to evaluate organizations against core HIPAA requirements.

Organizations that treat risk analysis, vendor management, and incident response as continuous disciplines, not annual checkboxes, will be better positioned as these trends evolve.

This article is for informational purposes only and does not constitute legal advice. Organizations should consult qualified counsel regarding specific compliance obligations.

When was the last time your organization updated its HIPAA security risk analysis?

Aris Medical Solutions can help you identify compliance gaps and prevent costly data breaches.
Schedule your HIPAA compliance review today and protect your organization from the next enforcement headline.

Your Trusted Partner for HIPAA Compliance since 2009
Is Your Medical Practice Prepared for the Cybersecurity Threats that are Increasing?

New cybersecurity statistics reveal why healthcare organizations must strengthen their security safeguards.

Cybercriminals continue to target healthcare organizations, regardless of their size. Small medical practices, dental offices, and business associates face many of the same threats as larger healthcare systems.

The 2026 Verizon Data Breach Investigations Report highlights growing cybersecurity risks and the importance of basic security safeguards. The report analyzed more than 31,000 security incidents and 22,000 confirmed data breaches worldwide. These findings demonstrate why healthcare organizations must take cybersecurity seriously.

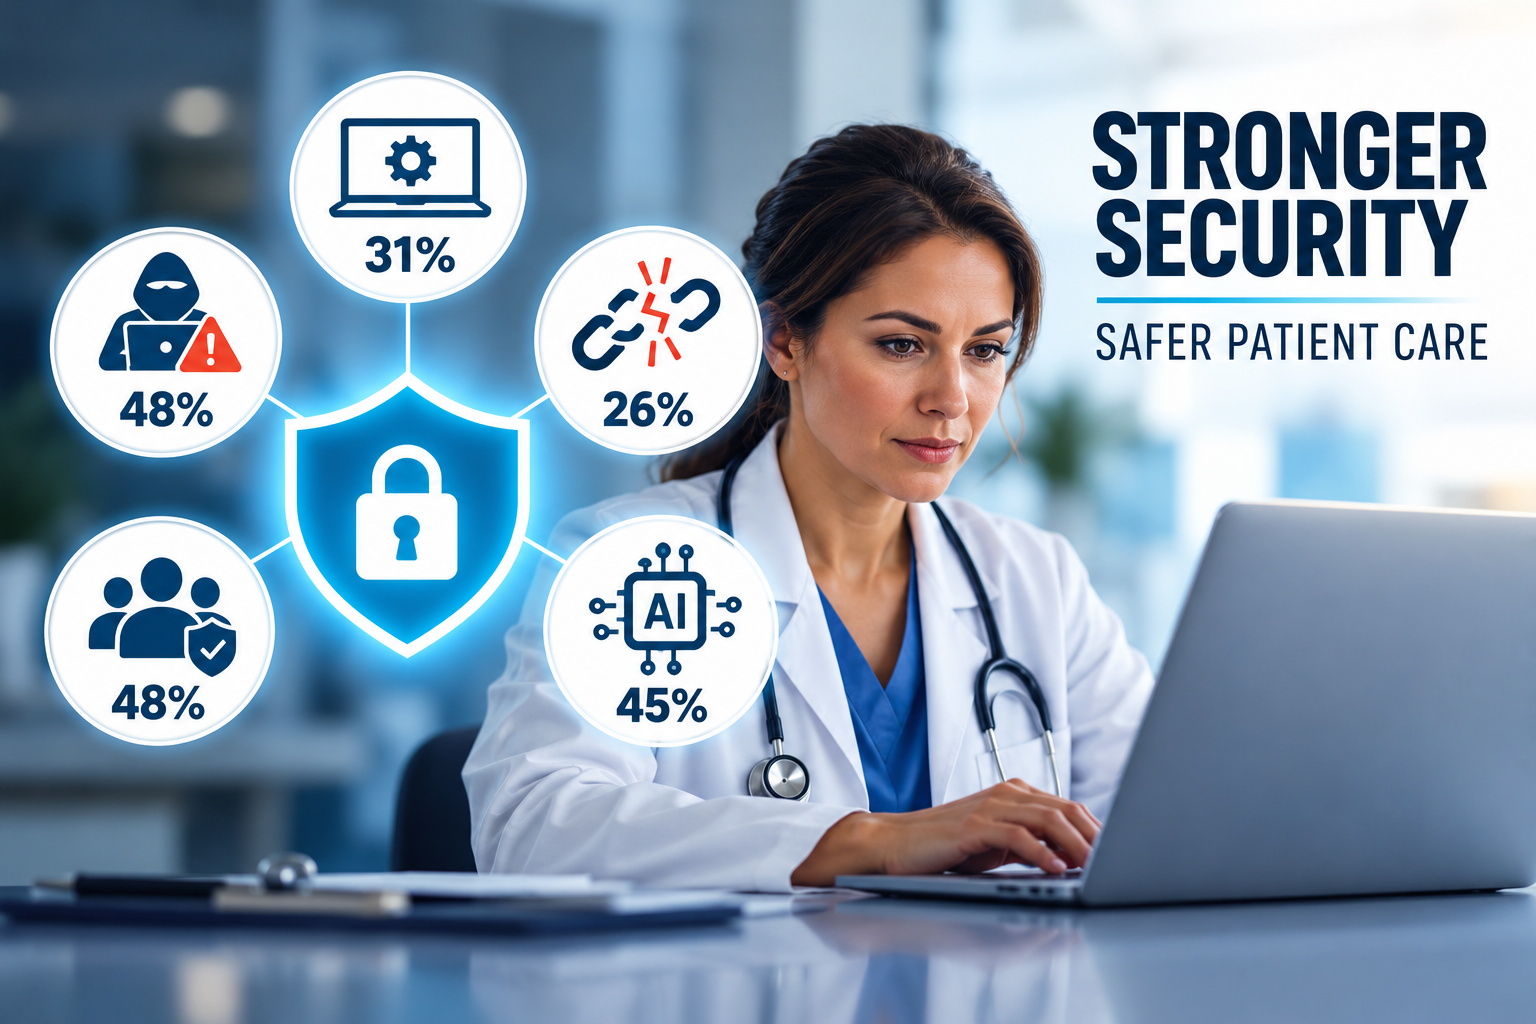
31% of Data Breaches Begin with Exploited Vulnerabilities

Cybercriminals frequently exploit weaknesses in software, networks, and security configurations. Verizon reports that vulnerability exploitation accounted for 31% of breaches in its 2026 analysis. This finding reinforces the importance of identifying and correcting security weaknesses before attackers exploit them. Healthcare organizations should conduct regular vulnerability assessments, install security patches, and review system configurations. However, vulnerability assessments alone do not satisfy HIPAA’s Security Risk Analysis requirements. Organizations must evaluate threats, vulnerabilities, existing safeguards, and potential risks to patient information. A comprehensive HIPAA Security Risk Analysis helps organizations identify risks to electronic Protected Health Information (ePHI).

48% of Data Breaches Involve Ransomware

Ransomware remains one of the most serious cybersecurity threats facing healthcare organizations. Verizon found ransomware involvement in 48% of confirmed breaches analyzed in its 2026 report. These attacks can encrypt medical records, interrupt patient care, and disrupt daily operations. Healthcare organizations must prepare for more than restoring computer systems. They need documented contingency plans that address emergency operations, data recovery, and system restoration. Regular backups, recovery testing, and employee training help organizations prepare for ransomware attacks. A disaster recovery plan should identify critical systems, recovery priorities, and responsible personnel. A written plan provides little protection unless the organization tests it and maintains it.

Only 26% of Known Exploited Vulnerabilities Were Fully Remediated

Identifying security weaknesses represents only the first step toward protecting patient information. Verizon reported that organizations fully remediated only 26% of tracked, known exploited vulnerabilities during 2025. The median time to resolve these vulnerabilities increased from 32 days to 43 days. These findings highlight a dangerous gap between identifying security risks and correcting them. Medical practices should maintain documented procedures for identifying, prioritizing, and correcting security vulnerabilities.

A Risk Management Plan helps organizations assign responsibilities, establish deadlines, and track corrective actions. HIPAA compliance requires organizations to address identified risks, not simply document their existence.

48% of Data Breaches Involve Third Parties

Healthcare organizations depend on outside vendors to manage technology, billing, records, and other essential services. Unfortunately, these relationships can introduce additional cybersecurity risks. Verizon found that third parties played a role in 48% of breaches analyzed in its 2026 report. Third-party breach involvement also increased significantly compared with the previous reporting period. Medical practices should evaluate the security practices of vendors that access, process, or store patient information.

A signed Business Associate Agreement establishes important legal responsibilities, but it does not guarantee adequate cybersecurity protection. Organizations should review vendor safeguards, incident reporting procedures, access controls, and subcontractor relationships. Regular vendor oversight helps identify weaknesses before they expose patient information.

Artificial Intelligence Creates New Security Challenges

Artificial intelligence offers healthcare organizations opportunities to improve efficiency and streamline administrative tasks. However, unauthorized AI tools can introduce significant privacy and security risks. Verizon reported that regular employee AI use on corporate devices increased from 15% to 45%. This figure includes authorized and unauthorized AI use. The report also identified unauthorized AI activity as a growing source of potential data exposure. Employees may unknowingly expose confidential information by entering sensitive data into unapproved AI applications. Healthcare organizations should establish clear AI policies and train employees on acceptable use. They should also evaluate AI vendors before allowing access to patient information. When applicable, organizations must obtain Business Associate Agreements and implement appropriate safeguards.

Basic Cybersecurity Safeguards Make a Difference

Healthcare organizations do not need to wait for a cyberattack to strengthen their defenses. They can reduce cybersecurity risks by implementing and maintaining essential safeguards.

These safeguards include:

  • Conducting comprehensive Security Risk Analyses.
  • Developing and updating Risk Management Plans.
  • Maintaining an asset list and include how data flows through your network.
  • Performing vulnerability assessments and applying security patches.
  • Implementing multifactor authentication and appropriate encryption.
  • Maintaining secure system configurations and access controls.
  • Training employees to recognize phishing and other cyber threats.
  • Reviewing Business Associate and vendor security practices.
  • Developing and testing contingency and disaster recovery plans.
  • Monitoring system activity and investigating suspicious behavior.
  • Establishing policies for artificial intelligence and sensitive information.

These actions help organizations protect patient information and maintain essential healthcare operations.

HIPAA Compliance Is More Than Checking a Box

Many healthcare organizations mistakenly believe that purchasing cybersecurity software satisfies their HIPAA obligations. However, technology represents only one component of an effective HIPAA compliance program. Organizations must also establish policies, train employees, evaluate risks, and document corrective actions.

A comprehensive compliance program combines administrative, physical, and technical safeguards. The HIPAA Security Rule requires covered entities and business associates to protect electronic patient information. These requirements apply regardless of an organization’s size.

Small practices cannot assume that cybercriminals will overlook them.

The Bottom Line: Prevention Costs Less Than Recovery

A cybersecurity incident can create significant financial, operational, and reputational consequences. Medical practices may face business interruptions, recovery expenses, regulatory investigations, and damaged patient trust.

Although no security program can eliminate every threat, proactive safeguards can significantly reduce risks. Healthcare organizations should focus on preventing incidents while preparing to respond when something goes wrong.

Protecting patient information is not a one-time project. It requires continuous attention, documented safeguards, and ongoing risk management.

The question is not whether your organization can afford cybersecurity.

The question is whether your organization can afford the consequences of inadequate protection.

When was the last time your organization updated its HIPAA security risk analysis?

At Aris Medical Solutions, our HIPAA Keeper™ cloud-based platform makes HIPAA compliance simple. It guides your organization through every requirement with a clear, step-by-step process. From risk analyses, risk management, policies to employee training and required documentation, you’ll have everything needed to remain compliant, protected, and audit-ready. Best of all, your HIPAA Compliance Officer is never on their own. Every client has access to a Certified HIPAA Security Analyst who provides expert guidance, answers questions, and helps ensure your compliance program is implemented correctly.

Schedule your HIPAA compliance review today and protect your organization from the next enforcement headline.

Your Trusted Partner for HIPAA Compliance since 2009
Sources

  1. Verizon, 2026 Data Breach Investigations Report.
  2. Verizon, 2026 DBIR Healthcare Industry Snapshot.
  3. Center for Internet Security, CIS Controls and MS-ISAC Insights Featured in Verizon’s 2026 Data Breach Investigations Report.

Note: The reported percentages reflect different datasets and measures. They do not represent breach rates for all medical practices.

OIG Exclusion List vs. CMS Preclusion List: What Medical Practices Need to Know

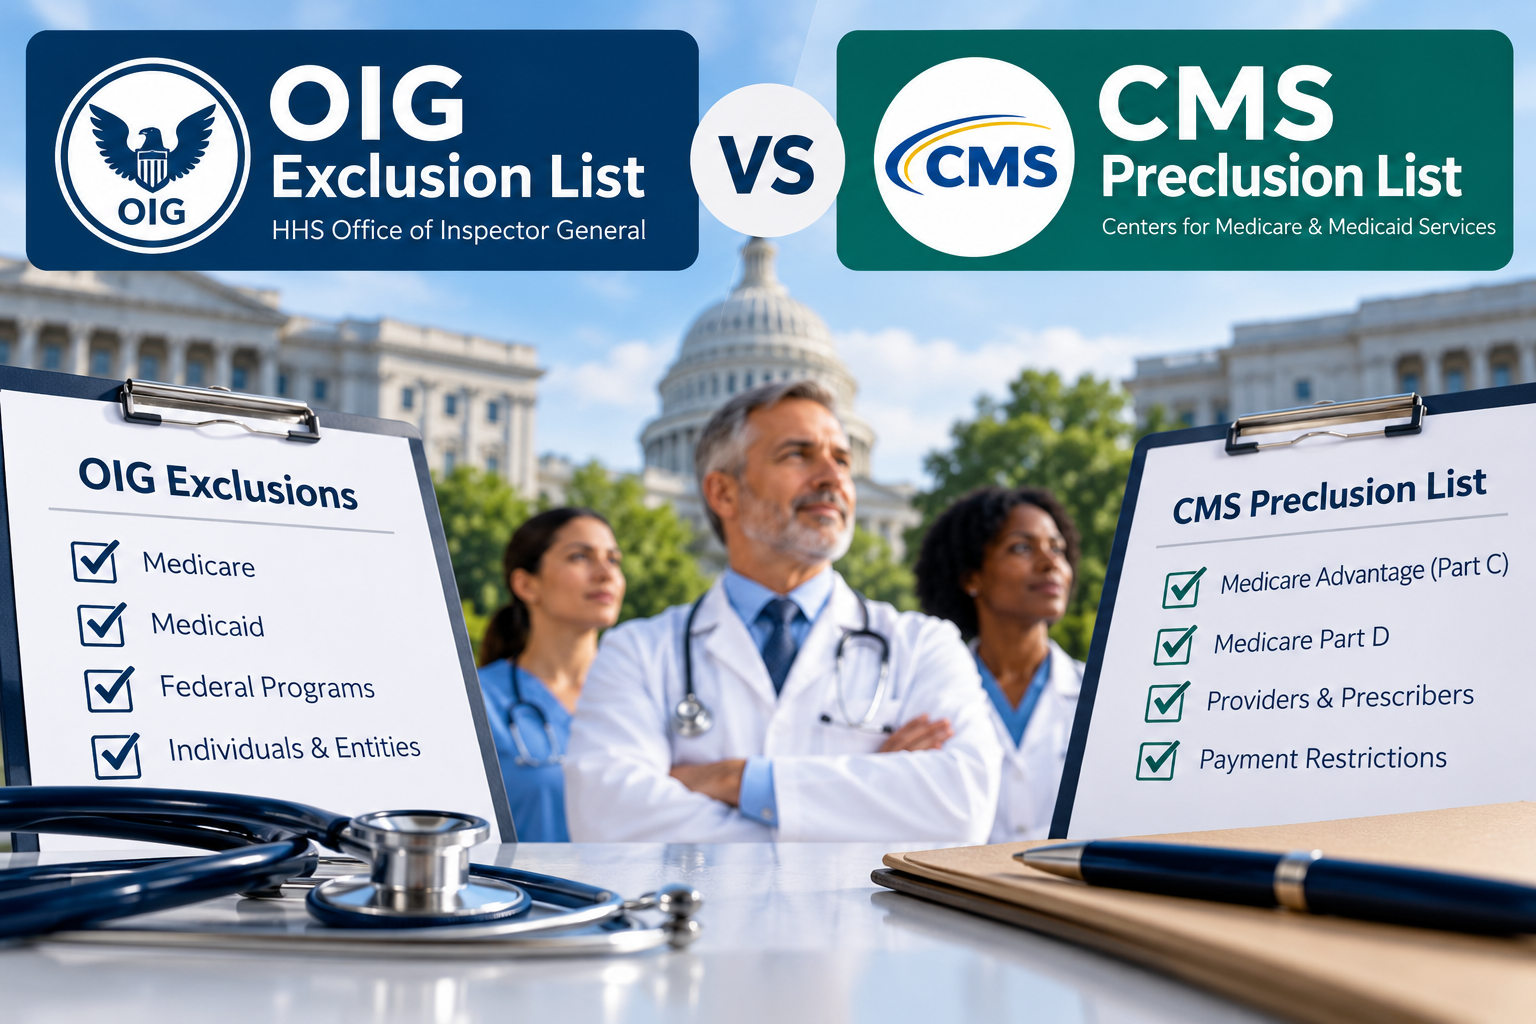
Medical practices must understand the differences between the OIG Exclusion List and the CMS Preclusion List. Both programs help protect federal healthcare programs from fraud, abuse, and improper payments. However, each program serves a different purpose and carries different consequences.

Understanding the OIG Exclusion List

The Department of Health and Human Services (HHS) Office of Inspector General (OIG) maintains the List of Excluded Individuals/Entities (LEIE).

The OIG uses this list to identify individuals and organizations excluded from participating in federal healthcare programs. These programs include Medicare, Medicaid, and other federally funded healthcare programs.

The list may include physicians, nurses, administrative employees, contractors, vendors, and healthcare organizations.

The OIG may exclude individuals or organizations for several reasons, including:

  • Healthcare fraud and certain criminal convictions.
  • Patient abuse or neglect.
  • Certain professional licensing violations.
  • Other violations that qualify for exclusion under federal law.

Federal healthcare programs generally cannot pay for services or items furnished by excluded individuals or entities.

Medical practices can search the OIG database to verify exclusion status. Practices should screen employees, providers, and relevant contractors before engagement and monthly thereafter.

Monthly screening helps practices identify exclusions and reduce financial and regulatory risks.

Understanding the CMS Preclusion List

The Centers for Medicare & Medicaid Services (CMS) maintains the CMS Preclusion List.

CMS uses this list to identify providers and prescribers who meet specific Medicare preclusion criteria.

The list primarily affects Medicare Advantage (Part C) and Medicare Part D prescription drug coverage.

CMS may place providers or prescribers on the list for several reasons, including:

  • Revocation of Medicare enrollment under qualifying circumstances.
  • Certain felony convictions.
  • Conduct that meets CMS preclusion criteria.

Medicare Advantage plans generally cannot pay for healthcare items or services furnished by providers on the Preclusion List. Medicare Part D plans must also reject covered prescriptions from precluded prescribers, subject to applicable requirements.

Unlike the OIG database, CMS does not provide a publicly searchable Preclusion List.

Instead, CMS distributes the list to applicable Medicare Advantage and Part D organizations. These organizations must review the list and apply the required payment restrictions.

Why Medical Practices Must Understand Both Lists

The OIG Exclusion List affects participation and payments across multiple federal healthcare programs. The CMS Preclusion List focuses primarily on Medicare Advantage payments and Medicare Part D prescriptions.

An individual may appear on one list without appearing on the other.

Medical practices should establish screening procedures that address applicable federal and state requirements.

Regular screening helps practices identify potential compliance concerns before they create costly problems.

Protecting your practice requires more than checking employee credentials.

It also requires verifying eligibility to participate in federal healthcare programs.

By understanding both lists, medical practices can strengthen compliance efforts, reduce financial risks, and protect their organizations.

Does your organization have a process in place to manage your documentation?

Aris Medical Solutions can help you identify compliance gaps and prepare for upcoming changes.

Schedule your HIPAA compliance review today and protect your organization from the next enforcement headline.

Your Trusted Partner for HIPAA Compliance since 2009
FTC $20M Fine Highlights the Risk of Using AI without Verification

$20 Million Settlement Highlights Risks of False Medical Billing and AI-Generated Documentation

DOJ Settlement: $20 Million, Including $10 Million in Restitution

The U.S. Department of Justice (DOJ) announced a $20 million settlement involving Heal 360 urgent-care and primary-care clinics. The settlement resolves allegations that the clinics submitted fraudulent claims for COVID-19 testing services.

The DOJ alleged that Heal 360 billed a federal COVID-19 program for medical services the clinics never performed.

Patients reportedly received only COVID-19 specimen collection services. However, the clinics billed higher-level evaluation and management (E/M) codes, including 99203, 99204, 99213, and 99214.

These codes represented more extensive medical services than patients allegedly received.

How Medical Documentation Contributed to the Alleged Fraud

The DOJ identified several practices that raised serious concerns about billing accuracy and medical record integrity.

According to the allegations:

  • False Medical Records: Staff used electronic templates to document examinations and medical services that never occurred.
  • Remote Scribes: Overseas remote scribes entered information into patient records, including documentation supporting services the clinics allegedly never provided.
  • Incorrect Rendering Providers: The clinics identified a physician as the rendering provider on most claims, despite no patient examination or treatment.
  • Improper Billing: The clinics submitted hundreds of thousands of claims using higher-level E/M codes instead of appropriate collection codes.

These allegations highlight the importance of accurate medical documentation, proper coding, and provider oversight.

What This Means for Healthcare Providers

This settlement raises important concerns for medical practices, urgent-care centers, billing companies, coding vendors, and remote-scribe services.

Organizations using electronic templates or AI-assisted documentation should pay particular attention.

Technology can simplify medical documentation, but providers must verify that every record accurately reflects the services performed.

AI-generated notes and automated templates do not eliminate the provider’s responsibility for accurate documentation and billing.

Steps Healthcare Organizations Should Take Now

Healthcare organizations should review their documentation and billing procedures to reduce compliance risks.

  1. Verify Billing Accuracy: Compare billed E/M codes against the services performed and documented.
  2. Audit Medical Records: Review templated and copied notes for examinations, patient histories, or medical decisions that never occurred.
  3. Confirm Provider Responsibility: Require rendering providers to review and authenticate documentation supporting their claims.
  4. Review AI and Remote-Scribe Documentation: Verify the accuracy of AI-generated notes and information entered by remote scribes.
  5. Monitor Billing Vendors: Ensure billing companies select codes based on documented services, not automatically populated template fields.
  6. Address Overpayments: Investigate potential billing errors and promptly correct and return identified overpayments when required.
  7. Maintain Audit Trails: Preserve records identifying who created, reviewed, modified, and authenticated each medical note.

AI Documentation Creates New Compliance Responsibilities

Healthcare organizations increasingly rely on AI, remote scribes, and electronic templates to improve efficiency.

These technologies can reduce administrative workloads, but they also introduce documentation and compliance risks.

Providers must ensure that automated records accurately reflect each patient’s encounter.

A completed medical record does not prove that a documented service actually occurred.

Organizations should establish clear policies for reviewing AI-generated documentation, verifying clinical accuracy, and maintaining accountability.

The Bottom Line

This settlement does not prohibit healthcare organizations from using remote scribes, electronic templates, or AI-assisted documentation.

However, electronically generated records can become evidence in False Claims Act investigations when they misrepresent services.

Healthcare providers must maintain accurate records, verify billing codes, and ensure that documentation supports every submitted claim.

Remember: Technology can assist with documentation, but it cannot replace provider accountability.

The defendants deny the allegations, and the settlement does not establish liability.

Source: U.S. Department of Justice – Heal 360 $20 Million Settlement

Contact Aris Medical Solutions for a complimentary HIPAA compliance consultation.

Schedule your HIPAA compliance review today and protect your organization from the next enforcement headline.

Hurricane Preparedness

For those of you in the path of this storm here are some guidelines to prepare for a hurricane.

Prep your office

  • Print your Contingency Plan or have it available in an alternate location. Make sure you have your emergency contact list that includes vendors you may need.
  • Take your inventory list with you, if possible, take pictures of all equipment with serial and model numbers. You may need this for an insurance claim.
  • If necessary, create a backup and take it with you. Secure it if it is not encrypted.
  • Print out patient schedules, in case of internet outage. 
  • Print out your manual forms/procedures in case systems are down. Place in plastic tubs.
  • Shut down servers and workstations properly and disconnect power (contact your IT vendor to advise them you are shutting down). This includes firewalls / switches / printers / scanners, etc. Place equipment on a desk and cover with plastic bags or place them in plastic tubs if you are not taking them with you. If you have a rack system, place large garage bags over the racks and secure.
  • Remove laptops / external hard drives / software installation disks / operating system disks. There is nothing worse than trying to reload a server or workstations operating system and software and not be able to find the discs. Be sure to label them before removing them so you know where to return them to. Be sure to shut laptops down to engage encryption (if encryption is activated). Secure external hard drive and media. Be sure the person taking the equipment is not in the path of the storm, or travel as far inland as possible.
  • Move any equipment away from windows if possible. If you are expecting a storm surge, it is recommended to take as much of your equipment with you as possible. It would be a good idea to identify who carries servers like yours and note the lead times in case you have to buy a new one.
  • Move anything of value OFF the floor in case of flooding. Place it in plastic tubs.
  • It may be necessary to turn off the main breaker as well.

Prep your home

  • Make extra ice or fill empty containers and freeze them. This can be used to keep your refrigerator and/or freezer cooler longer.
  • Fill the cooler with ice. If you lose power, put the items that you use the most to prevent opening your refrigerator.
  • Make sure all devices and portable chargers are charged.
  • Have battery powered lights or flashlights on hand (extra batteries as well).
  • Important papers, including insurance policies should be stored in the cloud or in a waterproof container.
  • Have a container ready with medications, water, and food for at least 3-5 days.
  • If you have a generator, be sure to test it and have additional fuel on hand.
  • Heavy items and furniture, such as a patio table, may be turned on their sides or upside down to help prevent it from being caught by the wind and tossed about the patio.
  • Potted plants – even small pots can become dangerous projectiles in hurricane strength winds; therefore, they should be removed.
  • Patio umbrellas – close them and remove them from stands and/or patio tables. A gust of wind can send an open umbrella flying through your screen enclosure.
  • Flagpoles – remove flags, and lower or remove pole, if possible.
  • Decorative items – store them safely inside your home or garage to ensure protection from water damage.
  • Enclosed swimming pool – Pool builders recommend leaving water in your pool during a hurricane or strong storm but adding more chlorine to reduce storm water contamination. Your pool may overflow but will be less likely to be damaged by the storm and/or debris that may fall into it. Most importantly, cover outdoor electrical devices with appropriate waterproof material to reduce the risk of damage.

This should be reviewed each year

Overhanging trees, cut back limbs, remove decaying branches, trim off weak limbs and loose leaves. Pay extra attention to any trees or shrubs that are close to your home and especially your patio area and screen enclosure or pool.

Stay safe and watch for downed power lines. These can be deadly!

NIST OCR conference highlights

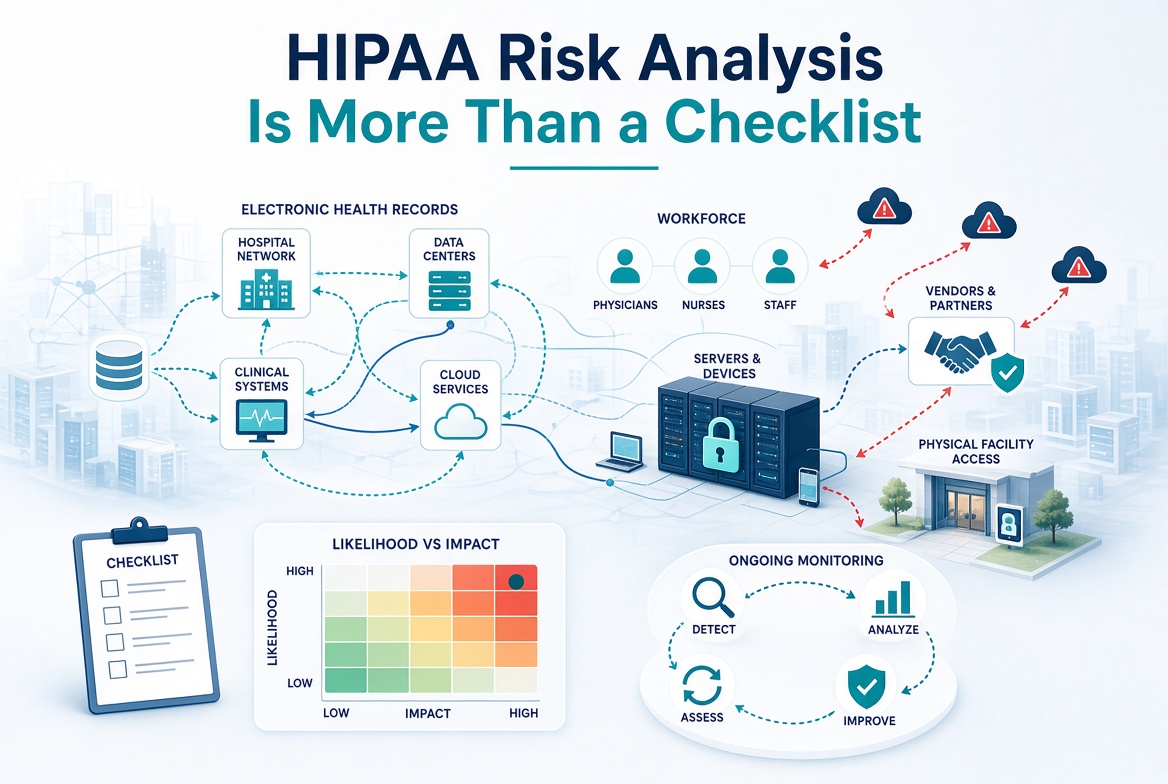
HIPAA Risk Analysis Is More Than a Checklist

The message from the NIST OCR conference was clear: a HIPAA risk analysis is not a checklist. It must be comprehensive, accurate, and specific to your organization. Once a thorough and accurate risk analysis is completed, then the mitigation process must be documented. Again, not simply a checklist.

Where is ePHI?

The risk analysis must identify every location where electronic protected health information (ePHI) is created, received, maintained, or transmitted. This includes EHR systems, email, mobile devices, cloud applications, medical equipment, patient portals, billing platforms, databases, websites, backups, and third-party vendors.

Medical practices must map how ePHI flows into, throughout, and outside their systems. This data-flow mapping helps identify unauthorized access, transmission, storage, and disclosure risks that a simple checklist may overlook.

Risk Management

Identifying vulnerabilities is only the beginning. The practice must maintain a documented risk management plan that:

  • Prioritizes identified risks
  • Lists the corrective actions taken
  • Assigns responsibility
  • Establishes completion dates
  • Demonstrates how each vulnerability was mitigated
  • Documents any remaining risk the organization accepts

What is NOT a Risk Analysis?

Several security assessments can support the process, but they do not replace an SRA:

  • A penetration test is useful, but it is not an SRA.
  • A vulnerability scan is useful, but it is not an SRA.
  • A gap analysis is helpful, but it is not an SRA.
  • Completing the HHS SRA Tool does not create a compliant risk analysis if questions are unanswered or marked “Don’t Know.”

Another common problem is leaving the physical safeguards section incomplete. An SRA must evaluate administrative, physical, and technical safeguards and not just cybersecurity controls.

Integrating AI

Before adding an AI tool to a medical practice, the organization should complete the proper privacy, security, and compliance review. Determine whether the AI vendor will access, store, or transmit ePHI. Understand where the data is stored and whether it is used to train AI models. Update the organization’s risk analysis and data-flow map. Establish user access controls, authentication, encryption, and audit logging. Whether ePHI will be shared with third party vendors. Create policies for appropriate AI use and human review. Once this is outlined, then the organization must:

  • Develop procedures for errors, security incidents, and potential breaches
  • Train employees on privacy risks and prohibited uses
  • Obtain a Business Associate Agreement
  • Address patient consent and state-law requirements when applicable

AI can improve efficiency, but it should not be integrated until the practice understands how patient information will be handled and has documented safeguards in place.

Breach Notification

The breach notification clock starts when the breach is discovered, not when the investigation is completed. An organization should not delay the required notification solely because the final number of affected individuals is unknown. File the initial breach report within the applicable deadline using the best information available, and submit an addendum when the investigation confirms the affected-record count or provides additional details. Be sure to follow state law requirement if they are more stringent.

FTC and HIPAA

The FTC does not enforce HIPAA. That responsibility belongs to HHS’s Office for Civil Rights (OCR). However, the FTC can intervene when a healthcare organization’s conduct involves an unfair or deceptive business practice under the FTC Act. A provider could face FTC scrutiny if it misrepresents how patient information is protected. For example, the practice has a “Seal of HIPAA Compliance” on their website and fails to use reasonable security safeguards. The use of online trackers may be sharing health information with advertising or tracking companies contrary to their privacy promises. Therefore, HIPAA compliance does not automatically protect an organization from FTC enforcement. The FTC’s separate Health Breach Notification Rule (HBNR) generally applies to health apps, personal health-record vendors, and related businesses that are not regulated by HIPAA; in some situations, an organization with both HIPAA-regulated and consumer-facing operations may have obligations under both regulatory frameworks.

Summary

The NIST OCR conference clarified the HIPAA compliance requirements. It is crystal clear that more enforcement in on the way due to the increased data breach activity and the lack of documented compliance efforts. They even specifically mentioned that even small providers are required to implement reasonable and appropriate safeguards. No provider is immune from investigations and enforcement.

Protect Your Organization and Your Patients Before It’s Too Late

At Aris Medical Solutions, our HIPAA Keeper™ cloud-based platform makes HIPAA compliance simple. It guides your organization through every requirement with a clear, step-by-step process. From risk analyses and policies to employee training and required documentation, you’ll have everything needed to remain compliant, protected, and audit-ready. Best of all, your HIPAA Compliance Officer is never on their own. Every client has access to a Certified HIPAA Security Analyst who provides expert guidance, answers questions, and helps ensure your compliance program is implemented correctly.

Schedule a free HIPAA checkup today at Aris Medical Solutions.

Don’t let the 2027 HIPAA updates catch you off guard

Webinar date:

Join Suze Shaffer on Sept 16, 2026 at 1:00 pm to learn how evolving regulatory expectations may impact your organization and discover practical strategies to strengthen your risk analyses, business associate agreements, cybersecurity, data access controls, and AI governance to reduce breach risk and prepare for audits or regulatory investigations.

Why propose an update to the HIPAA Security rule?

The U.S. Department of Health and Human Services (HHS) has proposed a major overhaul of the HIPAA Security Rule, the first since 2013. There has been much discussion about the proposed updates, they have been postponed, but they are NOT canceled. These sweeping new security rule changes are a tough response to the rapidly growing number of large-scale data breaches and cyberattacks now targeting healthcare services and organizations across America.

Don’t let your medical organization get caught off guard! 

In just 60 minutes, you’ll discover what you need to know and what you need to do to navigate the coming HIPAA Security Rule changes. You will learn how to:

  • Navigate the Coming 2027 HIPAA Security Rule Changes: Get a clear update on the proposed overhaul and what it means for medical office managers and their organizations.
  • Many of the proposed changes are already enforceable, but these updates will make them mandatory and may increase fines.
  • Strengthen Risk Analyses and Business Associate Agreements: Discover practical strategies to improve risk analyses and BAAs so your practice is better prepared for stepped-up audits and investigations.
  • Improve Cybersecurity, Data Access Controls, and AI Governance: Learn how to reduce breach risk with stronger cybersecurity practices, access controls, and AI governance.
  • And MUCH MORE!

Cost: $97 (Free for Premium Members)

Register here: Medical Office Manager

  • What: Webinar — What Every Medical Office Manager Needs to Know NOW about Sweeping New 2027 HIPAA Security Rule Changes
  • When: Wednesday, September 16, 2026, 1:00–2:00 p.m. Eastern Time
  • Who: Suze Shaffer, President, Aris Medical Solutions
  • Where: From the comfort of your computer, at your office, or at your home office!
  • Why: To update medical office managers on the latest changes to the 2027 HIPAA Security Rule and regulations—and show practical steps to reduce breach risk and prepare for audits.

Register here: Medical Office Manager

AI in Medical Offices and Patient Privacy

Artificial intelligence (AI) is no longer a futuristic concept in healthcare; it is already reshaping day-to-day operations in medical offices and throughout healthcare. From automating appointment scheduling and streamlining billing to supporting clinical decision-making and analyzing medical images, AI tools promise greater efficiency, reduced administrative burden, and potentially better patient outcomes. Yet every application that touches patient data brings a corresponding obligation: careful protection of patient privacy. Healthcare AI tools are already facing lawsuits, and with state and federal AI regulations changing rapidly, shielding your practice from costly privacy litigation is becoming increasingly challenging, unless you understand how to minimize that risk and protect patient privacy. The key is implementing AI responsibly before legal or regulatory issues arise.

Practical Applications of AI in Medical Offices

Medical practices are adopting AI across both administrative and clinical workflows:

Administrative automation — AI-powered chatbots and voice systems handle appointment booking, reminders, insurance verification, and basic patient inquiries. Natural language processing tools can draft clinical notes from physician dictation or ambient conversation, reducing documentation time.

Clinical decision support — Algorithms analyze electronic health record (EHR) data to flag potential drug interactions, suggest differential diagnoses, or identify patients at elevated risk for certain conditions.

Imaging and diagnostics support — AI assists in reading X-rays, dermatology photos, or retinal scans, often as a “second reader” that highlights areas of concern for the clinician.

Operational insights — Predictive models forecast no-show rates, optimize staffing, and identify revenue-cycle bottlenecks.

Patient engagement — Personalized educational materials, remote monitoring alerts, and symptom checkers help patients stay engaged between visits.

Privacy Requirements: The Foundation of Trust

Under HIPAA, any AI system that creates, receives, maintains, or transmits PHI is subject to the Privacy Rule, Security Rule, and Breach Notification Rule.

Key obligations include:

1. Business Associate Agreements (BAAs) Most AI vendors act as business associates. Medical offices must execute a BAA before sharing any PHI. The agreement must require the vendor to implement appropriate safeguards, report breaches, and restrict use of data to the purposes authorized by the covered entity.

2. Minimum Necessary Standard AI systems should be configured to access only the data required for the specific task. Broad data lakes or unrestricted model training on full patient records violate this principle unless a clear, documented justification exists.

3. Security Safeguards The Security Rule requires administrative, physical, and technical protections. This typically means:

  • Encryption of data at rest and in transit
  • Strong access controls and multi-factor authentication
  • Audit logging of every access and model inference involving PHI
  • Regular technical risk analyses that specifically address AI-related threats

4. Patient Rights and Transparency Patients retain rights to access their records, request amendments, and receive an accounting of disclosures. When AI tools influence clinical decisions or generate notes that become part of the record, practices should be prepared to explain how those tools work at a high level and how patients can exercise their rights.

5. De-identification and Secondary Use If a practice or vendor wants to use data for model improvement or research, proper de-identification (Safe Harbor or Expert Determination methods) or a valid authorization is required. Simply stripping obvious identifiers is often insufficient for modern AI systems that can re-identify individuals through pattern recognition.

International practices or those serving patients across borders must also consider GDPR, state privacy laws (such as CCPA/CPRA in California or emerging comprehensive state laws), and any sector-specific rules.

Best Practices for Implementing AI Responsibly

  • Conduct a thorough risk assessment before deployment, focusing on data flows, model training sources, and potential failure modes.
  • Prefer on-premises or private-cloud deployments when feasible, or insist on strong contractual and technical isolation in multi-tenant cloud environments.
  • Maintain human oversight. AI recommendations should remain decision-support tools, not autonomous clinical actors, unless the system has undergone appropriate regulatory review (FDA clearance for certain medical devices, for example).
  • Train staff on both the capabilities and the limitations of the AI tools they use, including how to recognize and report anomalous outputs that might indicate data leakage or bias.
  • Establish clear policies for prompt engineering and data entry so that staff do not inadvertently include unnecessary PHI in interactions with generative AI systems.
  • Monitor continuously. Privacy is not a one-time checkbox; ongoing auditing, penetration testing, and vendor assessments are essential.

Balancing Innovation and Obligation

The tension between rapid AI adoption and privacy protection is real. Practices that treat privacy as an afterthought risk regulatory penalties, reputational damage, and most importantly the erosion of trust that underpins the patient-clinician relationship. Those that embed privacy-by-design principles from the start can capture the efficiency and clinical benefits of AI while meeting their ethical and legal duties.

Medical offices do not need to choose between technological progress and patient confidentiality. The most successful implementations will be those that treat privacy requirements not as obstacles, but as essential design constraints that ultimately strengthen both the technology and the care it supports.

As AI continues to evolve, so will the regulatory landscape. Practices that build strong governance, demand accountability from vendors, and keep patients informed will be best positioned to use these powerful tools safely and effectively.

Protect your practice — and your patients

At Aris Medical Solutions, our HIPAA Keeper™ cloud-based platform makes HIPAA compliance simple. It guides your organization through every requirement with a clear, step-by-step process. From risk analyses and policies to employee training and required documentation, you’ll have everything needed to remain compliant, protected, and audit-ready. Best of all, your HIPAA Compliance Officer is never on their own. Every client has access to a Certified HIPAA Security Analyst who provides expert guidance, answers questions, and helps ensure your compliance program is implemented correctly.

Schedule a free HIPAA checkup today at Aris Medical Solutions.

Cybersecurity – Why Human Habits Matter

When we think of cybersecurity, we often picture sophisticated hackers exploiting complex software bugs. In reality, the battlefield is much closer to home: it’s your busy routine, your packed inbox, and your daily habits. Cybercriminals rarely “break in” using high-tech tools; instead, they trick well-meaning employees into opening the digital front door for them. Whether it’s a fake job offer on LinkedIn, an urgent financial message, or a reused password, modern threats exploit our busy schedules and human nature. One click is all it takes to give a cybercriminal a foothold in your organization. Effective cybersecurity isn’t about imposing impossible restrictions; it’s about making secure habits the easiest choice every day. Building a culture where security becomes second nature is one of the most effective ways to reduce risk and protect your organization.

Why Your Staff Is the Target

Hackers don’t wait for a technical weakness; they wait for a human moment.

The “Human Element”: A massive 68% of security breaches involve human behavior.

Personal and Professional Mix: We use the same devices for work and life. If you click a bad link in your personal Facebook feed on a work laptop, the hacker is instantly inside the business.

The Busy Trap: You don’t have to be careless to get hacked; you just have to be busy. Phishing works because it catches people when they are distracted.

Password Recycling: If you use the same password for your Netflix and your company email, a leak at Netflix gives hackers a direct key to your business.

Why Strict “Bans” Usually Fail

When IT departments try to block everything, like banning personal social media or certain apps, it often backfires.

The Workaround: Instead of stopping the behavior, people just find “shadow” ways to do it, like using their personal phones.

Loss of Visibility: When employees hide their activity to get around strict rules, IT loses the ability to see and manage the real risks.

How to Actually Lower the Risk

The most effective security matches how people actually work.

Separate Your Digital Lives: Use different browser profiles for work and personal stuff. This keeps your “home” habits from accidentally bleeding into “work” data.

Expect a Leak: Assume a password will be stolen eventually. By turning on Multi-Factor Authentication (MFA), you make an account 99% less likely to be hacked even if the password is leaked. Protecting the MFA method is extremely important since hackers trick people into clicking on links that actually share their MFA process.

Unique Keys: Use a different password for every single account so one “bad apple” doesn’t spoil the whole bunch. Many people are turning to FIDO2 keys. FIDO2 security keys (hardware authenticators like YubiKeys) enable strong, phishing-resistant authentication using public-key cryptography, often for passwordless login or as a second factor. FIDO2 combines the WebAuthn API (for websites/browsers) and CTAP (for communicating with external keys via USB, NFC, or Bluetooth). A single key can hold credentials for many sites.

How to use a FIDO2 Key:

Registration

  1. The website (relying party) requests registration.
  2. The key generates a unique public/private key pair scoped to that site/origin.
  3. The private key stays on the hardware key and never leaves it.
  4. The public key (plus attestation data) is sent to and stored by the website.

Authentication

  1. The site sends a one-time random challenge.
  2. The user proves presence or verifies identity (touch the key, enter a PIN, or use biometrics if supported).
  3. The key signs the challenge with its private key.
  4. The site verifies the signature against the stored public key and grants access.

Because the private key never leaves the device and credentials are origin-bound, intercepted data or phishing sites cannot reuse them.

If you find this information helpful, please share it with your colleagues and friends. Together we can keep our information private!

Protect Your Organization Before It’s Too Late

At Aris Medical Solutions, our HIPAA Keeper™ cloud-based platform makes HIPAA compliance simple. It guides your organization through every requirement with a clear, step-by-step process. From risk analyses and policies to employee training and required documentation, you’ll have everything needed to remain compliant, protected, and audit-ready. Best of all, your HIPAA Compliance Officer is never on their own. Every client has access to a Certified HIPAA Security Analyst who provides expert guidance, answers questions, and helps ensure your compliance program is implemented correctly.

Protect your practice — and your patients.

Schedule a free HIPAA checkup today at Aris Medical Solutions.

Google Reviews on Medical Websites: HIPAA Compliance Risks

Patients trust online reviews. A strong Google rating can influence where someone chooses to receive care. As a result, many medical practices display Google reviews directly on their websites to build credibility and attract new patients.

While this may seem harmless, healthcare organizations should carefully evaluate the HIPAA implications before embedding or displaying patient reviews. What appears to be a simple marketing strategy can create privacy and compliance risks.

Can Medical Practices Display Google Reviews on Their Website Without Violating HIPAA?

Patients may voluntarily post reviews about their own healthcare experiences on Google. HIPAA does not prevent patients from sharing their own health information publicly.

The compliance issue arises when a healthcare provider republishes those reviews on its own website.

Republishing a patient’s review may be viewed as using or disclosing protected health information (PHI) for marketing or promotional purposes. Even though the patient made the information public, HIPAA does not automatically grant the provider permission to reuse it.

The fact that information is publicly available does not eliminate a covered entity’s HIPAA obligations.

Does a Google Review Contain PHI?

Protected Health Information is individually identifiable health information that relates to an individual’s past, present, or future health, healthcare, or payment for healthcare.

Many patient reviews include statements such as:

  • “Dr. Smith treated my diabetes.”
  • “The staff helped me through chemotherapy.”
  • “I had cataract surgery here.”
  • “My child received ADHD treatment.”

When a healthcare provider republishes these reviews, the practice is associating an identified individual with healthcare services it provided. That combination may constitute PHI.

What If Only Initials Are Used?

Some practices believe replacing the patient’s full name with initials eliminates the HIPAA concern.

Unfortunately, it may not.

Initials often do not fully de-identify an individual. Combined with other information, such as the provider’s specialty, procedure performed, date of service, location, or the original review still available on Google, the individual may remain identifiable.

HIPAA’s de-identification standard requires that there be no reasonable basis to identify the individual. Simply changing “John Smith” to “J.S.” rarely satisfies that standard.

No.

Posting a review on Google demonstrates that the patient chose to share information with the public. It does not necessarily authorize the healthcare provider to reuse that information for its own marketing.

HIPAA authorizations have specific regulatory requirements. They generally must:

  • Clearly describe the information being used or disclosed.
  • Identify who may use the information.
  • Identify who may receive it.
  • Explain the purpose of the disclosure.
  • Include an expiration date or event.
  • Inform the individual of their right to revoke the authorization.
  • Be signed by the patient or personal representative.

A Google review does not meet these requirements.

Embedded Google Reviews May Create Additional Privacy Risks

Many practices use Google review widgets that automatically pull reviews onto their websites.

These widgets may introduce additional privacy concerns beyond the review itself.

Depending on how the widget functions, it may:

  • Load content directly from Google servers.
  • Place cookies on visitors’ browsers.
  • Collect IP addresses or device identifiers.
  • Share website activity with third parties.
  • Trigger analytics or advertising technologies.

If review widgets operate alongside analytics, advertising pixels, or other tracking technologies, practices should carefully evaluate whether protected health information could be disclosed to third parties.

Healthcare organizations should inventory all third-party technologies operating on their websites and determine whether appropriate safeguards, contracts, and configurations are in place.

OCR Has Increased Scrutiny of Website Tracking

The U.S. Department of Health and Human Services Office for Civil Rights (OCR) has repeatedly emphasized that healthcare organizations are responsible for understanding how third-party technologies collect and transmit information from their websites.

Authenticated patient portals, appointment scheduling systems, online bill payment pages, and other areas where visitors interact with healthcare services require particular attention.

Even public-facing websites deserve careful review when technologies collect information that could become individually identifiable in a healthcare context.

Best Practices for Medical Practices

If your practice wants to highlight positive patient experiences, consider these recommendations:

  • Obtain a HIPAA-compliant authorization before republishing identifiable patient testimonials.
  • Avoid copying reviews directly from Google without authorization.
  • Do not assume publicly posted information removes HIPAA obligations.
  • Evaluate whether review widgets transmit visitor information to third parties.
  • Conduct periodic website privacy and security reviews.
  • Review all analytics, advertising pixels, chat tools, and embedded third-party content.
  • Work with legal counsel or your HIPAA compliance team before implementing new marketing technologies.

Another Approach

Consider asking satisfied patients to provide a separate written testimonial using a HIPAA-compliant authorization form designed specifically for marketing purposes.

This approach provides clear documentation that the patient understands how the testimonial will be used and protects both the patient and the practice.

The Bottom Line

Google reviews are valuable marketing tools, but healthcare providers must approach them differently than most businesses.

A patient may choose to publicly discuss their healthcare experience, but that does not automatically give the provider permission to republish that information on its own website. In addition, embedded review technologies may introduce separate privacy risks that require careful evaluation.

HIPAA compliance extends beyond policies and training. It includes understanding how everyday marketing decisions can affect patient privacy.

Before displaying patient reviews on your website, make sure your practice has evaluated both the HIPAA authorization requirements and the privacy implications of the technology used to display them.

Disclaimer: This article is intended for educational purposes and does not constitute legal advice.

Protect Your Organization Before It’s Too Late

At Aris Medical Solutions, our HIPAA Keeper™ cloud-based platform makes HIPAA compliance simple. It guides your organization through every requirement with a clear, step-by-step process. From risk analyses and policies to employee training and required documentation, you’ll have everything needed to remain compliant, protected, and audit-ready. Best of all, your HIPAA Compliance Officer is never on their own. Every client has access to a Certified HIPAA Security Analyst who provides expert guidance, answers questions, and helps ensure your compliance program is implemented correctly.

Protect your practice — and your patients.

Schedule a free HIPAA checkup today at Aris Medical Solutions.

©2026 Aris Medical Solutions – HIPAA Risk Management | HIPAA Compliance Consultants | All Rights Reserved | Terms and Conditions | Privacy Policy
The content and images on this website is owned by Aris Medical Solutions and their owners. Do not copy any content or images without our consent.
Powered by Bandwise LLC