Call Us Today! 877-659-2467

What are the Identified Risks in Healthcare Data Breaches?

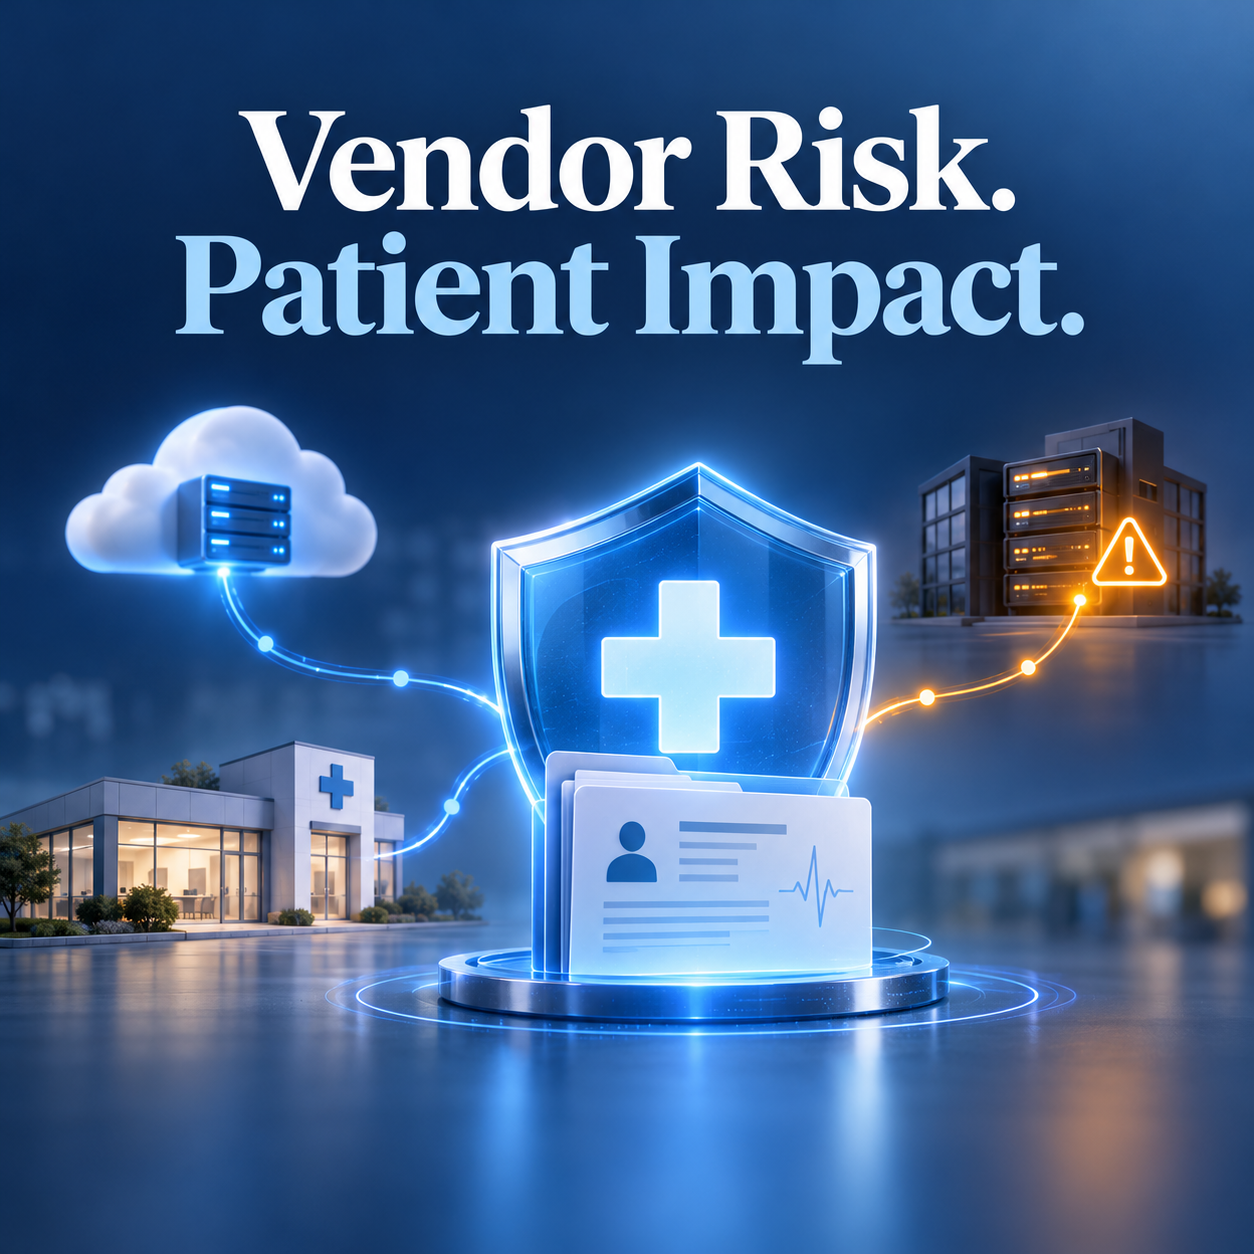
Vendor Risk Is the New Front Line

Healthcare organizations continue to report substantial data breaches in 2026. Hacking and IT incidents dominate reports to the HHS Office for Civil Rights (OCR). Large breach reports have eased slightly compared with 2025. However, third-party vendors and business associates continue to concentrate risk across healthcare.

The Healthcare Breach Landscape

During the first half of 2026, organizations reported 397 large healthcare breaches to OCR. These incidents affected approximately 33.8 million individuals. Although those figures declined from the previous year’s first half, they still represent substantial exposure.

Business associates played a role in approximately 43% of large breach reports. Hacking and IT incidents accounted for most cases. Several incidents illustrate how vendors, applications, and shared technology can expose patient information.

Notable 2026 examples illustrate the pattern:

DentaQuest

A May 2026 cyber incident affected approximately 15 million individuals connected to DentaQuest, a Sun Life subsidiary. The ShinyHunters extortion group claimed responsibility for the incident. The compromised information included names, addresses, Social Security numbers, and Medicare or Medicaid identifiers. It also included dental or vision information, such as diagnoses, treatment details, and billing records. DentaQuest began notifying individuals in July after the group reportedly leaked data following failed negotiations.

iRhythm Technologies

A June 2026 incident affected approximately 8.18 million people connected to iRhythm Technologies. Attackers used social engineering to access business applications hosted by third parties. The incident did not involve clinical systems or medical devices. The exposed information included names, contact details, birth dates, insurance numbers, account identifiers, serial numbers, and service dates. The company began notifications in October. At that time, it reported no evidence of identity theft.

Blueberry Pediatrics

An incident involving Blueberry Pediatrics affected approximately 341,000 individuals, including children. Attackers exploited a vulnerability in Metabase, a business intelligence and reporting tool. A related incident involving prescription partner Photon stemmed from the same vulnerability. The exposed information included names, birth dates, health plan details, and certain medical and billing information. Blueberry Pediatrics discovered the incident in August 2026 and began notifications in October.

Earlier Breaches Continue to Create Financial Consequences

Conduent’s 2024–2025 breach affected approximately 62.2 million individuals. The incident recently prompted an $80 million class-action settlement agreement.

Change Healthcare’s 2024 ransomware attack remains the largest reported healthcare breach, affecting approximately 192.7 million individuals.

These incidents show how one organization’s security failures can affect patients and healthcare partners nationwide.

OCR Continues to Prioritize Risk Analysis

OCR continues its Risk Analysis Initiative. Recent settlements repeatedly identify failures to conduct accurate and thorough risk analyses under the HIPAA Security Rule. The requirement appears at 45 CFR § 164.308(a)(1)(ii)(A). Several 2026 settlements highlight these recurring weaknesses.

Ambry Genetics

Ambry Genetics agreed to a $700,000 settlement following a phishing incident affecting approximately 225,000 people. OCR also identified concerns involving access termination and unique user identifiers.

OSF HealthCare System

OSF HealthCare System agreed to a $552,250 settlement involving a ransomware incident affecting approximately 54,000 individuals. OCR identified failures involving risk analysis, impermissible disclosures, and breach notification.

Spencer Gifts LLC

Spencer Gifts LLC agreed to a $450,000 settlement involving its employer-sponsored health plan after a ransomware attack. The case demonstrates that HIPAA obligations can extend beyond traditional healthcare providers.

Patient Access Still Drives Enforcement

OCR also continues its Right of Access Initiative. Shen Smiles, a Pennsylvania dental practice, agreed to a $140,000 settlement involving delayed patient access to records. OCR also identified related Privacy Rule deficiencies. The case reinforces a critical point: organizations can face HIPAA enforcement without experiencing a cyberattack.

What These Cases Mean for Healthcare Organizations

Vendor oversight requires ongoing attention.

Business associates, cloud applications, reporting tools, and billing partners create additional opportunities for unauthorized access. Identify which vendors create, receive, maintain, or transmit protected health information. Evaluate their safeguards and document your oversight. Address your organization’s HIPAA responsibilities when vendors handle patient information.

Risk analysis must reflect actual operations

An incomplete or outdated assessment can overlook significant threats. Include third-party applications, connected devices, remote access, and every location that stores or processes electronic protected health information. Evaluate phishing, social engineering, ransomware, and vendor vulnerabilities. Document identified risks, assign responsibility, and track corrective actions.

Contracts and notification procedures need clear ownership

Business associate agreements should clearly define incident reporting duties and applicable responsibilities. Organizations must also understand their own patient and OCR notification obligations. Practice your response before an incident forces urgent decisions.

Financial consequences extend beyond regulatory settlements

Breaches can trigger class action lawsuits, state investigations, operational disruptions, and substantial recovery expenses. Organizations may also pay for forensic investigations, notifications, monitoring, and system restoration. Patient trust can take much longer to rebuild.

Five Actions to Take Now

  1. Update your risk analysis. Include third-party systems, current threats, and changes in your operations.
  2. Review high-risk vendors. Request meaningful evidence of security controls and evaluate how those safeguards protect your information.
  3. Test your incident response procedures. Confirm reporting contacts, notification timelines, decision responsibilities, and procedures for vendor incidents.
  4. Strengthen patient access procedures. Train staff to recognize requests, track deadlines, document responses, and escalate delays.
  5. Review cyber insurance. Examine coverage limits, vendor-related incidents, exclusions, and policy conditions with your insurance professional.

Attackers exploit weaknesses throughout the healthcare ecosystem. OCR continues to evaluate organizations against core HIPAA requirements.

Organizations that treat risk analysis, vendor management, and incident response as continuous disciplines, not annual checkboxes, will be better positioned as these trends evolve.

This article is for informational purposes only and does not constitute legal advice. Organizations should consult qualified counsel regarding specific compliance obligations.

When was the last time your organization updated its HIPAA security risk analysis?

Aris Medical Solutions can help you identify compliance gaps and prevent costly data breaches.
Schedule your HIPAA compliance review today and protect your organization from the next enforcement headline.

Your Trusted Partner for HIPAA Compliance since 2009
What does “Recognized Security Practices” mean?

We have talked in the past about the Office for Civil Rights conducting a minimum of a 12 month look back for data security/ HIPAA compliance efforts. If an organization suffers a breach, with proper documentation fines may be waived. This is known as “Recognized Security Practices”. Every organization will have different documentation based on their network configuration and how data flows in and out of your information systems. This isn’t really anything new since data security requirements have been in place since the Security Rule was enacted. There have been updates over the last few years, and they are making some new revisions requiring covered entities and business associates to document their efforts now more than ever. NIST SP800-66 Rev. 2

This includes ensuring your policies and procedures are documented and followed by your staff. Our online system makes this task must easier by enabling the HIPAA compliance officer to download and share certain policies for employees to review. Plus, the confidentiality and acceptable use agreement that is signed via DocuSign demonstrates you have advised your employees they must follow your policies and procedures.

Another part of this documentation should be reports from your IT department/vendor. Again, depending on how you access ePHI (electronic protected health information), reports will vary from practice to practice. Some suggested reports are:

  1. Managed devices. You can use this as your inventory list instead of completing the list in your package. However, we still recommend documenting which devices have been used to access and/or store ePHI.
  2. In the report above, this may contain operating systems, patches / updates that have been applied, IP addresses, User ID, and a device name. All of this is useful information, and if the report does not contain this information, you need to look for another report.
  3. Software lists are very important since you can see if any employee has downloaded unauthorized software or if a computer has been compromised.
  4. Device health reports typically include information on anti-virus, last log in, some record failed logins, or that is in a different report. These are must have reports.
  5. Access logs may be located within the software the IT vendor utilizes to manage your network, within your domain controller, and within your EHR/PM software. These reports must be reviewed to ensure employees are only accessing ePHI based on their job function and to look for outside intrusions.
  6. Backup reports should demonstrate when backups are performed and to ensure they are successful.
  7. Summary reports are useful, but you must make sure you review them, and they can be lengthy.

There are times when certain devices cannot be updated or upgraded due to the nature of the equipment and the cost to do so. This would not necessarily be a violation if you demonstrate other means to protect your system. For example, either removing the outdated equipment from internet access or placing it on a separate network so it would not be accessible by other drives that contain ePHI. Your IT vendor should be able to guide you through the proper process based on your particular network.

Annual audits by a third party are highly recommended unless your IT vendor specializes in network security. Often, these two types of companies work well together. The IT vendor handles the day-to-day operations, and the network security companies hardens the systems.

Some organizations complain that this costs too much money. Trust me, this is much less expensive than a data breach. Plus, if you plan on obtaining cyber liability insurance, carriers are now asking detailed questions about data security and compliance efforts. If you do have a data breach and you do not have “qualified documentation”, your claim could be denied. Of course, the term “qualified documentation” is open to interpretation. They do have an outlandish wish list from what I have seen. Although I have always been a proponent of this insurance, I am starting to believe unless you already have a policy, you may not be able to obtain one. If you do apply now, you will need to have HEAVY data security in place. Which you should have anyway!

To find out more about how our online HIPAA Keeper™ can help your organization with HIPAA Compliance click here:

https://arismedicalsolutions.com/aris-hipaa-compliance-system-for-medical-offices/

Or to schedule a demo click the contact us tab and scroll down.

“Simplifying HIPAA through Automation, Education, and Support”

How to protect your organization from phishing attacks

It is a known fact that hackers target the healthcare sector because the data is so valuable. The cost of healthcare data breaches increased from a total average of $7.13M in 2020 to $9.23M in 2021. The average breach cost rose $1.07M for those who had remote access. Organizations in the U.S. has lost $2.4B to business email scams. They have estimated that cybercrime topped $6T worldwide.

So, how do hackers get in and what can you do to protect yourself?

Remember, there isn’t ONE magic setting to protect you from all threats, it takes layers of security!

Organizations must have solid network security in place. Firewalls are a necessity in today’s world. You can set specific parameters to ensure employees can go where they need to, and block where they do not. You can also set security policies that block other countries.

Utilizing real-time anti-virus and anti-malware software also helps. This won’t help if an employee clicks on a link or picks up malware on the internet unless the system alerts the user BEFORE they click! For example, if an employee is surfing the web (and no they should not surf on a work computer), and they visit a website that has been infected, your anti-virus / anti-malware software should alert you with a warning.

Although there are brut attacks, but most hackers come in via through a phishing attempt. Often, an employee makes a simple mistake like clicking on a link or an attachment in an email. Even though I talk about this ALL the time and say NEVER do this…people still do.
Email scammers use several ways to trick employees to gain access to information. Including getting employees to send wire transfers, send a list of employee’s social security numbers, or to make purchases they are not aware of. Alan Suderman at Fortune cited a case where thieves hacked the email account of the organization’s bookkeeper, then inserted themselves into a long email thread, sent messages asking to change the wire payment instructions for a grant recipient, and made off with $650,000.
You think this can’t happen to you, but I know of a practice that someone hacked an email account and changed the bank information for payments from an insurance carrier, they lost about $100K.

I know of a company that the CEO email was hacked and being monitored, once the scammers knew who they talked to on the phone and who they did not, then the call came in to make a $65K wire transfer. POOF! Just like that $65K was gone.
YES, THIS HAPPENS! Keep in mind, if the caller or the email is asking for private information or money, verify BEFORE releasing it.

• Unless you are expecting an email from someone, DO NOT CLICK!
• If you get an email from someone you know and were not expecting it, pick up the phone and call them!
• If there is a link, open a web browser and open your account from there.
• If it is URGENT and requires you to act immediately, it is more than likely a hacker/spammer.
• If it says your credit card has been charged for something and you didn’t charge it, call your card company or your bank, do not call the number in the email or call the number in the voice mail.
• If they have all your information except the code on the back and ask you to verify the card by giving them the number, DO NOT.
• Government, state, and local authorities will not call you and demand payment immediately. Ignore these completely.
• Again, if money or personal information is involved, VERIFY!

Scammers share their success stories with other scammers, while ransomware hackers will hit you again if you pay. There is no honor among thieves.

All sizes of organizations need to be on high alert, from large hospitals to small single provider practices. I have used this analogy before, the World Wide Web it the modern version of the Wild Wild West. The biggest difference is you can’t see the bad guys coming into town to prepare. You must prepare for the unknown and the unseen.
There are companies that offer Phishing training. Then, they try to get your employees to take the bait. This has been a success at most companies. Educating your staff is JOB ONE! They can be your best ally, or your weakest link. You can build a fortress around your data, and one click can bring it down.

Continuous security awareness training is vital in your fight against these bad actors. Organizations must teach employees to be watchful for phishing attacks and stopping them by simply not engaging in emails and on the web.

To find out more about how our online HIPAA Keeper™ can help your organization with HIPAA Compliance click here:

https://arismedicalsolutions.com/aris-hipaa-compliance-system-for-medical-offices/

Or to schedule a demo click the contact us tab and scroll down.

“Simplifying HIPAA through Automation, Education, and Support”

Small Medical Practices are Huge Targets!


By Aris Medical Solutions


Many organizations have the attitude that they are too small to be a target for a data breach. Just because you don’t hear about small and medium sized practices being targeted doesn’t mean it is not happening.

Most medical practices are busy treating patients and are not aware of the severity behind this type of threat. Since small and even medium sized practices do not have the infrastructure in place to protect their data, they are a larger target than think. Data breaches can go undetected for months, if not years since they are not watching for it. For instance, if a Pediatric Practice is hacked, those social security numbers can be used for years before it will be discovered.

Many business associates are also targeted because they have access to medical records in different manner. Again, small and midsized organizations that do not have appropriate safeguards in place can wreak havoc in a medical environment. So what can you do?

First of all, conduct a Security Risk Analysis to understand what are your vulnerabilities. This is critical in order to mitigate risks.
Next, have a network security audit performed. Even if you access your data in the cloud and not through an onsite server, you can still be hacked.
Invest in monitoring your network. Know who is accessing your data.
TRAINING IS A MUST! Your employees can be your best asset or your largest liability.

Not only is this required under HIPAA, it is considered best practice in protecting patient data.

Contact Aris Medical Solutions at 877.659.2467 or click here to find out how we can protect your organization.

“Protecting Organizations through Partnership, Education, and Support”

©2026 Aris Medical Solutions – HIPAA Risk Management | HIPAA Compliance Consultants | All Rights Reserved | Terms and Conditions | Privacy Policy
The content and images on this website is owned by Aris Medical Solutions and their owners. Do not copy any content or images without our consent.
Powered by Bandwise LLC