It is hard to believe we are in 2021, but I am sure you are like the rest of us and glad to see 2020 in the rear-view mirror.
As we move into this new year, we need to look ahead and learn from what has happened in the past. Last month we informed you about many HIPAA violations that the Office for Civil Rights (OCR) had investigated. Most of these violations could have been prevented. In fact, I was talking with a colleague that owns an audit log monitoring system and he informed me that during the pandemic they saw a 90% increase in snooping into patient records of the same last name. Fortunately for his clients, this was immediately stopped, and the employee(s) were sanctioned. This made me want to remind you of a few requirements under HIPAA.
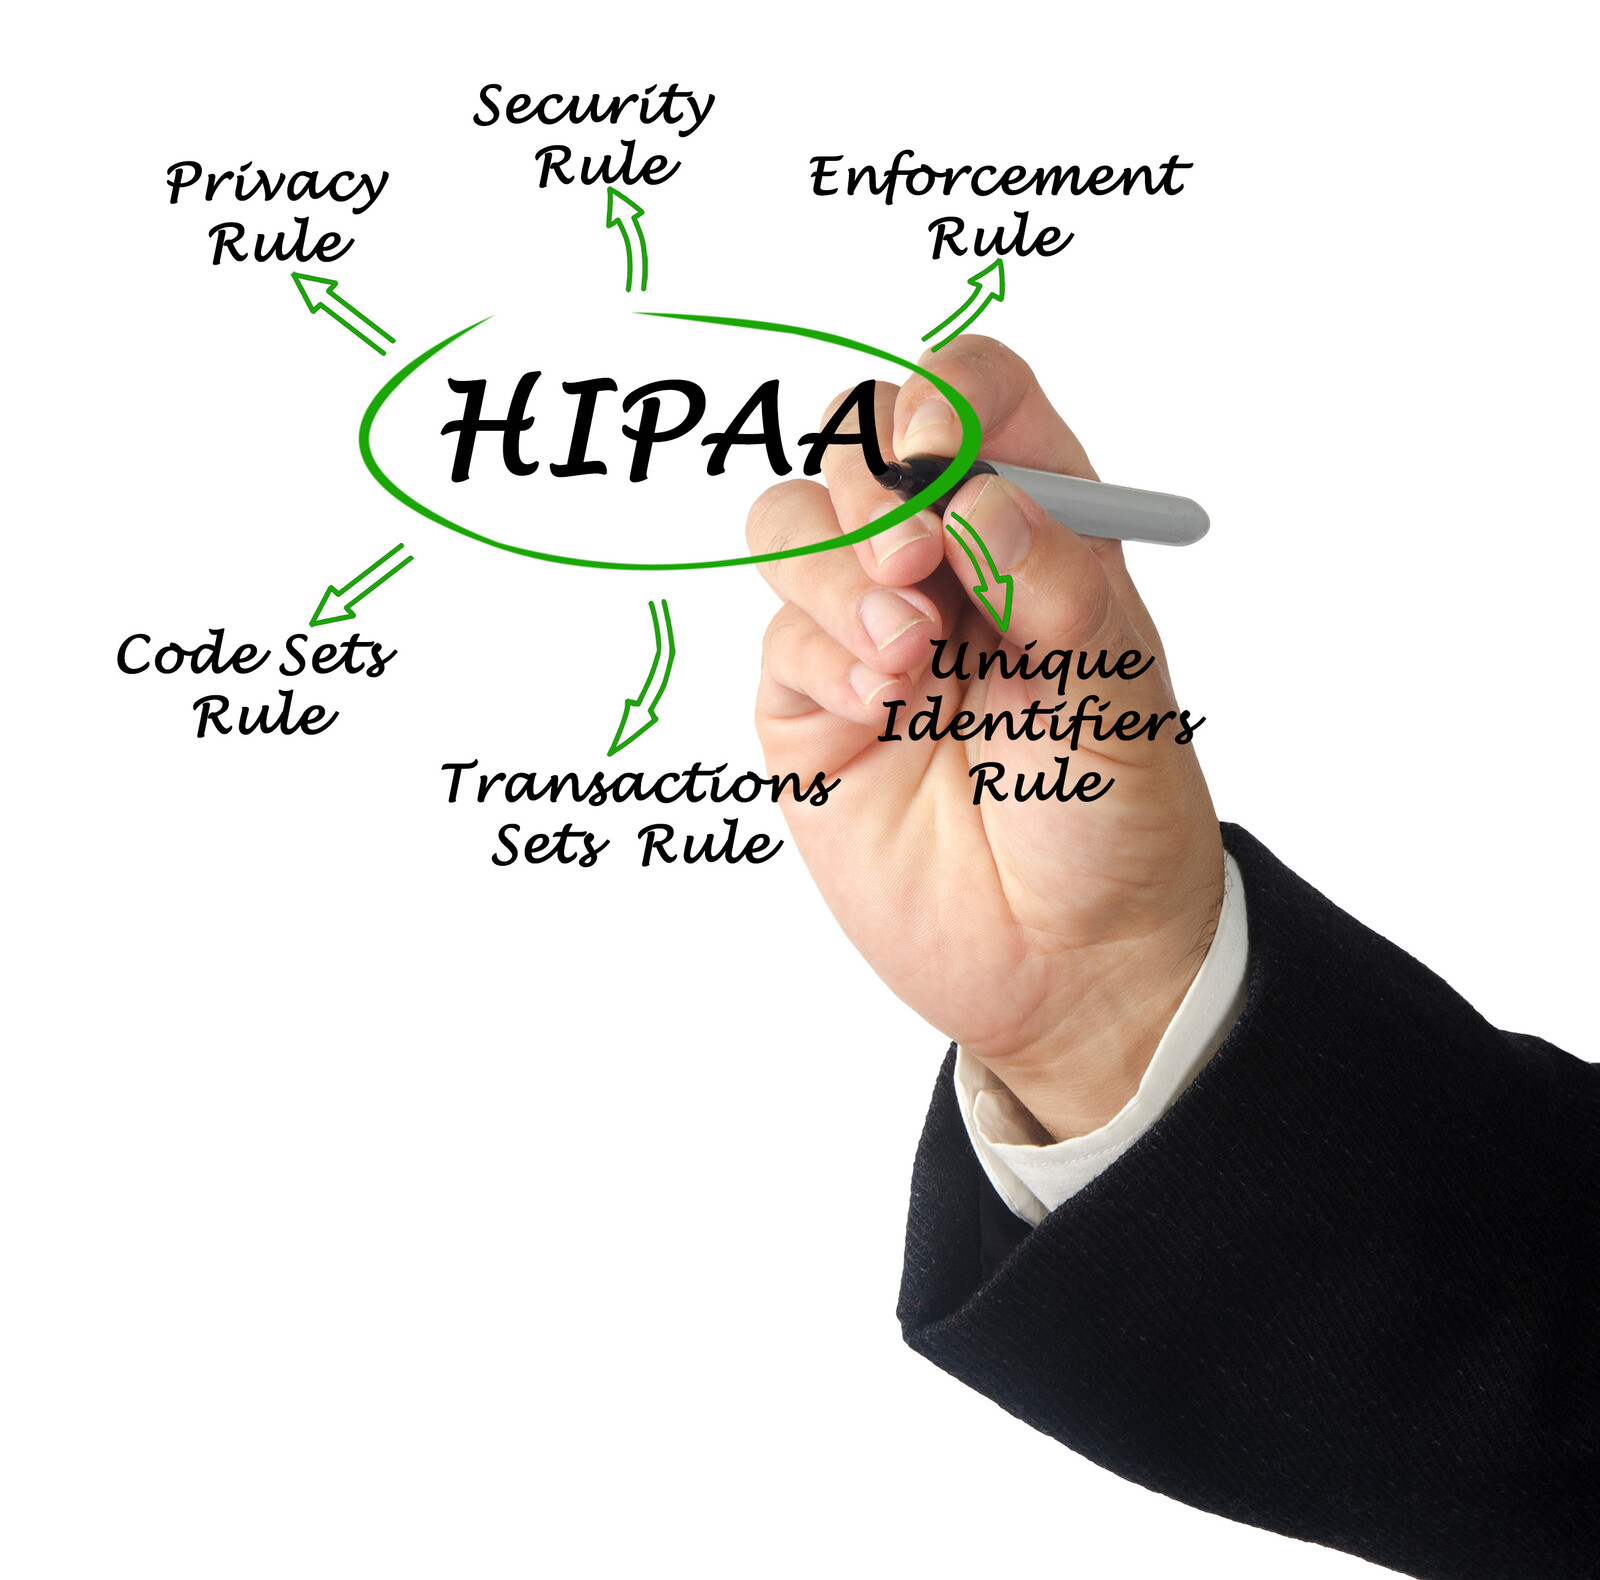
- 164.308(a)(1)(ii)(c) Sanction Policy – is a “required” standard under the HIPAA Security Rule. Employers are required by law to apply sanctions against employees who violate HIPAA, otherwise the employer could be fined.
- 164.308(a)(1)(ii)(d) Information System Activity Review – is another required standard. Which requires procedures to regularly review records of information system activity, such as audit logs, access reports, and security incident tracking reports. A security incident can be best described as the attempted or successful unauthorized access, use, disclosure, modification, or destruction of information or interference with system operations in an information system.
- 164.312(b) Audit Controls – is yet another required standard that states you must implement hardware, software, and/or procedural mechanisms that record and examine activity in information systems that contain or use electronic protected health information (ePHI). This standard goes hand in hand with Information System Activity Review.
What does this mean to you?
First, you must understand what is considered “normal” usage within your software/hardware that contains ePHI. Then you must monitor your systems for abnormal behavior. This is a HUGE time-consuming task and unless you are monitoring every employee, 24/7 you may miss something. We highly recommend utilizing a third party to do this for you. The company we work with has interfaces with over 60 EHRs and is fully automated. If they do not have an interface, they will create one, or show you how to upload the logs in a matter of minutes instead of hours. No more looking over lengthy audit log reports. You simply receive an alert when there is abnormal activity. Best of all, this protects your patient data and your practice from fines and penalties. If you would like to learn more about this service, use the contact us page.
If you need assistance with HIPAA Risk Management or guidance with your HIPAA Compliance, contact us at 877.659.2467 or complete the contact us form.