Call Us Today! 877-659-2467

State law data breach notification updates

All 50 states now have a separate privacy law. South Dakota and Alabama are the final two states to enact data breach notification laws. Other states like North Carolina are proposing to update their requirements that only allow 15 days to notify in the event of a data breach.

Although medical practices must adhere to the Federal HIPAA law guidelines, if your state law is more stringent state law will supersede federal notification requirements. You may also be required to notify your state officials or the credit reporting agencies. Know your state law!

Lastly, know where your patients or customers are located. Even if you are in a different state but you have their data, you must follow THEIR state privacy law. If you have any international patients or customers, be sure to understand how the GDPR will affect your organization. Then you must update your privacy policy within your office.

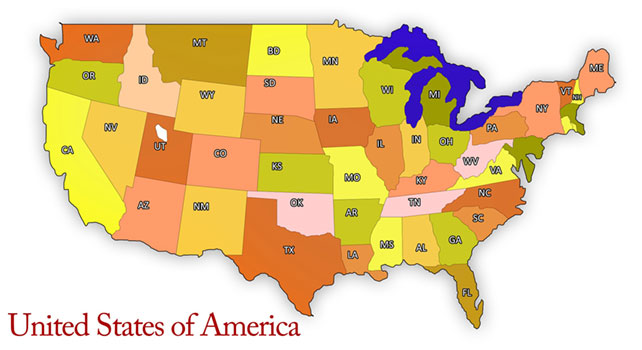
The link below lists the state and the statutes. Only a couple of the states have live links. If you want more information you will need to copy and paste in to Google.
http://www.ncsl.org/research/telecommunications-and-information-technology/2018-security-breach-legislation.aspx

To find out more about how our automated HIPAA compliance platform can help your organization click here:

https://arismedicalsolutions.com/aris-hipaa-service-automated-platform/

Or to schedule a demo click the contact us tab and scroll down.

“Simplifying HIPAA through Automation, Education, and Support

About Suze Shaffer

Suze Shaffer is the Owner and President of Aris Medical Solutions, a healthcare compliance company dedicated to simplifying HIPAA compliance. Through its online compliance solution, the HIPAA Keeper™, Aris Medical Solutions provides healthcare providers and business associates with the tools, documentation, training, and expert guidance needed to achieve and maintain HIPAA compliance.

Through the HIPAA Keeper™, Aris has assisted organizations nationwide with conducting risk analyses, developing risk management plans, implementing HIPAA Privacy and Security policies and procedures, and strengthening safeguards for protected health information. Aris Medical Solutions also considers applicable federal and state privacy and security requirements to help clients build a more comprehensive compliance program.

Suze is also a speaker and has presented at numerous conferences and professional events on HIPAA compliance, cybersecurity, risk management, and data breach prevention. Helping organizations understand their responsibilities and identify vulnerabilities before they result in a breach, audit, or investigation. She believes effective compliance begins with education. By helping organizations understand not only what they are required to do, but why those safeguards are important, organizations are better prepared to protect patient information and reduce their compliance risks.

At Aris Medical Solutions, the mission is simple: “Simplifying HIPAA” through education, expert guidance, and the HIPAA Keeper™, Aris Medical Solutions helps organizations turn complicated compliance requirements into a manageable, ongoing process.

The information provided reflects regulatory requirements and guidance available at the time of writing and is intended for educational purposes only. It should not be considered legal advice.

Share This HIPAA Blog

General Data Protection Regulation: What does this mean to the US

April 15, 2018

Workstation Security

June 19, 2018
©2026 Aris Medical Solutions – HIPAA Risk Management | HIPAA Compliance Consultants | All Rights Reserved | Terms and Conditions | Privacy Policy
The content and images on this website is owned by Aris Medical Solutions and their owners. Do not copy any content or images without our consent.
Powered by Bandwise LLC