Healthcare organizations continue to face significant data protection challenges in 2026, despite occasional monthly declines in breach reports. Through August, organizations reported approximately 593 large breaches to the HHS Office for Civil Rights (OCR). These breaches affected 500 or more individuals each and represented a 6.7% increase compared with the previous year. The incidents exposed protected health information (PHI) belonging to approximately 78.6 million people. That figure increased 14.8% compared with the same period in 2025.
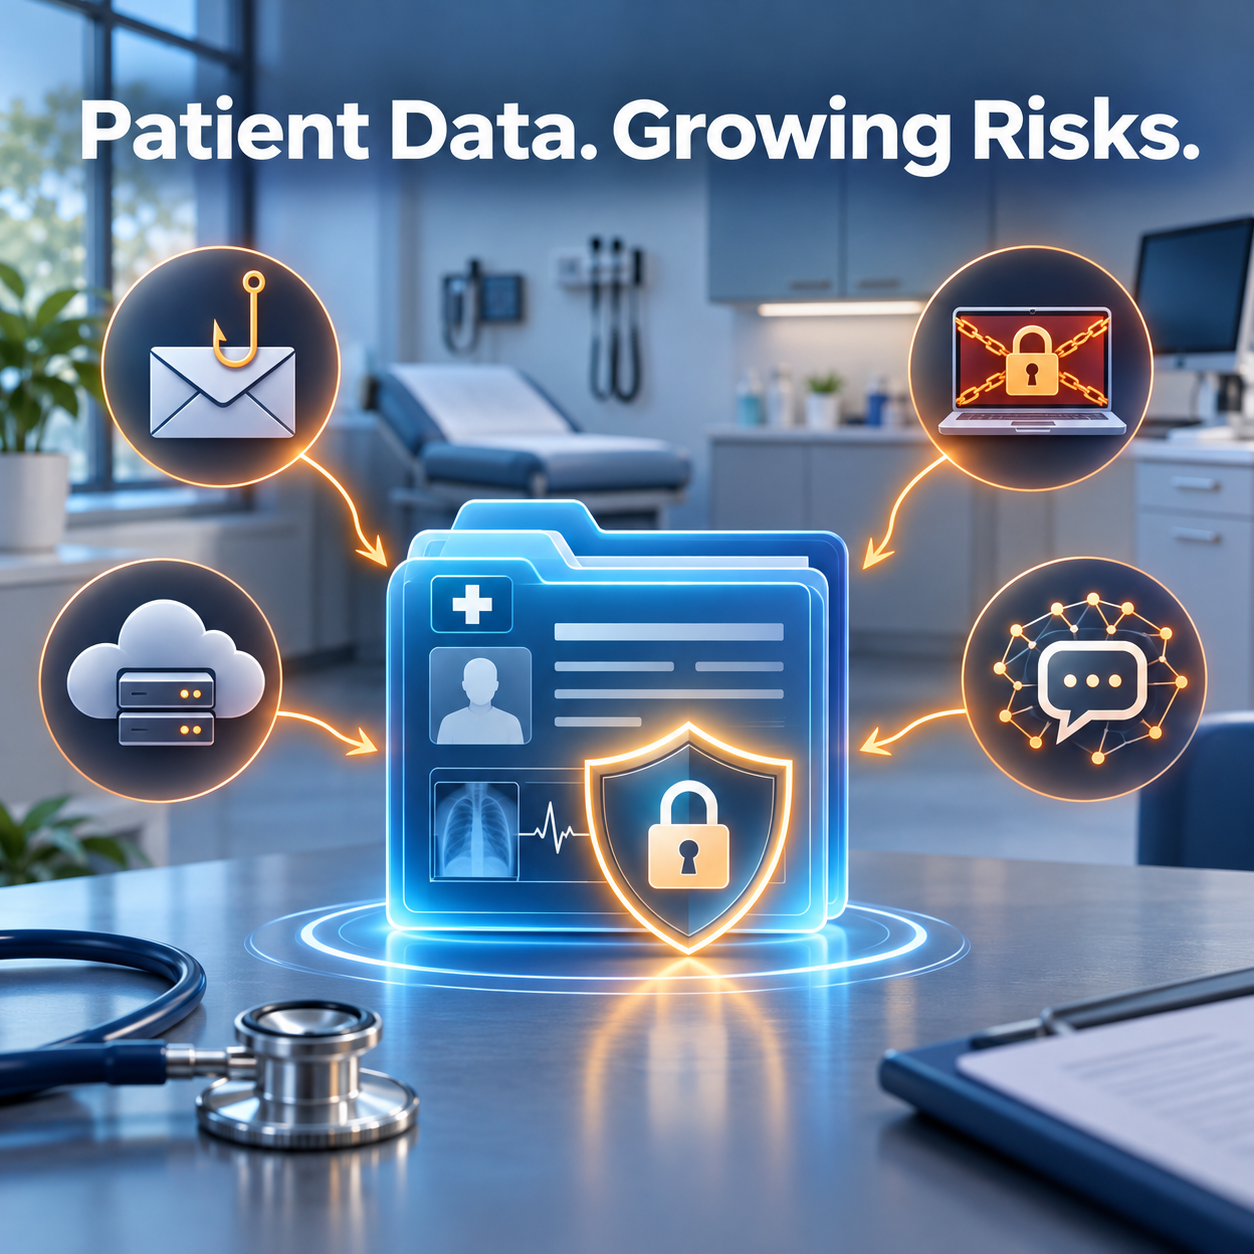
Hacking and IT incidents continue to dominate breach reports. However, attackers and workforce members increasingly expose information through different pathways. Third-party vendors and business associates account for a growing share of reports. Unauthorized AI use also creates risks alongside ransomware and phishing.
Recent Incidents and Settlements
iRhythm Technologies reported a June 2026 incident involving business applications that a third party hosted. Attackers used social engineering to gain unauthorized access. OCR portal filings identify more than 8.1 million affected individuals. Compromised information included names, contact details, birth dates, insurance numbers, account or device serial numbers, and service dates. According to reports, the incident did not affect clinical systems or devices.
AdaptHealth disclosed a hacking incident that exposed information belonging to more than 4.1 million individuals. The incident ranks among the year’s larger breach reports.
Lehigh Valley Health Network agreed to an $800,000 OCR settlement involving a 2023 ransomware incident. The attack affected 248,359 individuals. The settlement marked OCR’s 22nd ransomware enforcement action. OCR identified potential failures involving risk analysis, system activity reviews, and timely notifications to individuals and HHS. The organization also agreed to a $65 million settlement resolving related class-action litigation. Attackers stole sensitive clinical information, including some images of patients undergoing treatment.
Ambry Genetics agreed to a $700,000 settlement following a phishing attack affecting approximately 225,000 individuals. OCR identified deficiencies involving risk analysis, access termination, and unique user identification.
Patient Access Remains an Enforcement Priority
OCR continues to pursue complaints involving delayed patient access to medical records. Pennsylvania dental practice Shen Smiles paid $140,000, while Azul Vision paid $50,000. Both cases involved delays in providing patients with their records. These settlements reinforce OCR’s continued focus on patient access rights.
Emerging Risk: Unauthorized AI Use
A Johns Hopkins Bayview Medical Center staff member uploaded a spreadsheet to an unapproved public AI tool. The spreadsheet contained information about 3,182 patients who received admissions or treatments between May and September 2026. The information may have included names, medical record numbers, account numbers, admission dates, departments, medications, and provider names. The hospital reported that the information excluded Social Security numbers and financial account details. The hospital discovered the issue that same day. It directed deletion of the prompt and file, contacted the vendor, and began notifying patients. The hospital also offered credit monitoring.
This incident highlights the risks employees create when they use unauthorized AI tools for analysis or summarization. Uploading PHI outside approved systems can trigger breach assessments, notification obligations, and regulatory scrutiny. Organizations must also determine whether vendors retain copies after users delete uploaded information.
Common Gaps in OCR Investigations
OCR settlements repeatedly identify foundational weaknesses.
Organizations often fail to:
- Complete thorough risk analyses and update them as circumstances change.
- Implement effective access controls and audit logging.
- Notify affected individuals and regulators promptly.
- Establish clear policies for workforce use of new technologies.
Third-party involvement also remains a significant concern across recent large breaches.
Practical Steps for Healthcare Leaders
- Keep risk analysis current. Document findings and maintain a risk management plan that addresses identified vulnerabilities.
- Establish clear AI rules. Identify approved tools, restrict PHI uploads, and explain the risks of public platforms.
- Strengthen vendor oversight. Request evidence of risk assessments, establish incident reporting expectations, and maintain appropriate contractual safeguards.
- Improve notification procedures. Assign responsibilities, track deadlines, and address reporting requirements during incident response planning.
- Monitor patient access requests. Train staff, document requests, and resolve delays before they generate complaints.
Build Ongoing Accountability
The volume of incidents and affected individuals remains high even as monthly counts fluctuate. Organizations that invest in continuous risk assessment, clear technology governance (especially around AI), and disciplined vendor management are better positioned to reduce both the likelihood of incidents and the severity of regulatory and litigation outcomes when they occur.
When did your organization last review and update its HIPAA Security Risk Analysis?
At Aris Medical Solutions, our HIPAA Keeper™ cloud-based platform makes HIPAA compliance simple. It guides your organization through every requirement with a clear, step-by-step process. From risk analyses, risk management, policies to employee training, and required documentation, you’ll have everything needed to remain compliant, protected, and audit-ready. Best of all, your HIPAA Compliance Officer is never on their own. Every client has access to a Certified HIPAA Security Analyst who provides expert guidance, answers questions, and helps ensure your compliance program is implemented correctly.
Schedule your HIPAA compliance review today and protect your organization from the next data breach.
Your Trusted Partner for HIPAA Compliance since 2009