HIPAA Does Not Ban Email. It Does Require Thoughtful Safeguards.
Email can help your practice coordinate patient care. A mistyped address or an incorrect autofill suggestion can send protected health information (PHI) to the wrong person.
Treatment-related emails. The HIPAA Privacy Rule allows healthcare providers to email patients about their care when they use reasonable safeguards. HHS advises practices to verify the recipient’s address and limit sensitive details in unencrypted messages. Practices must also follow applicable HIPAA Security Rule requirements when sending electronic PHI.
Patient requests for copies of records. A separate rule applies when a patient exercises their HIPAA right of access. If the patient requests their records by unencrypted email, briefly explain that someone could intercept the message. If the patient confirms their choice after the warning, honor the request and verify the email address before sending.
Recommended safeguards:
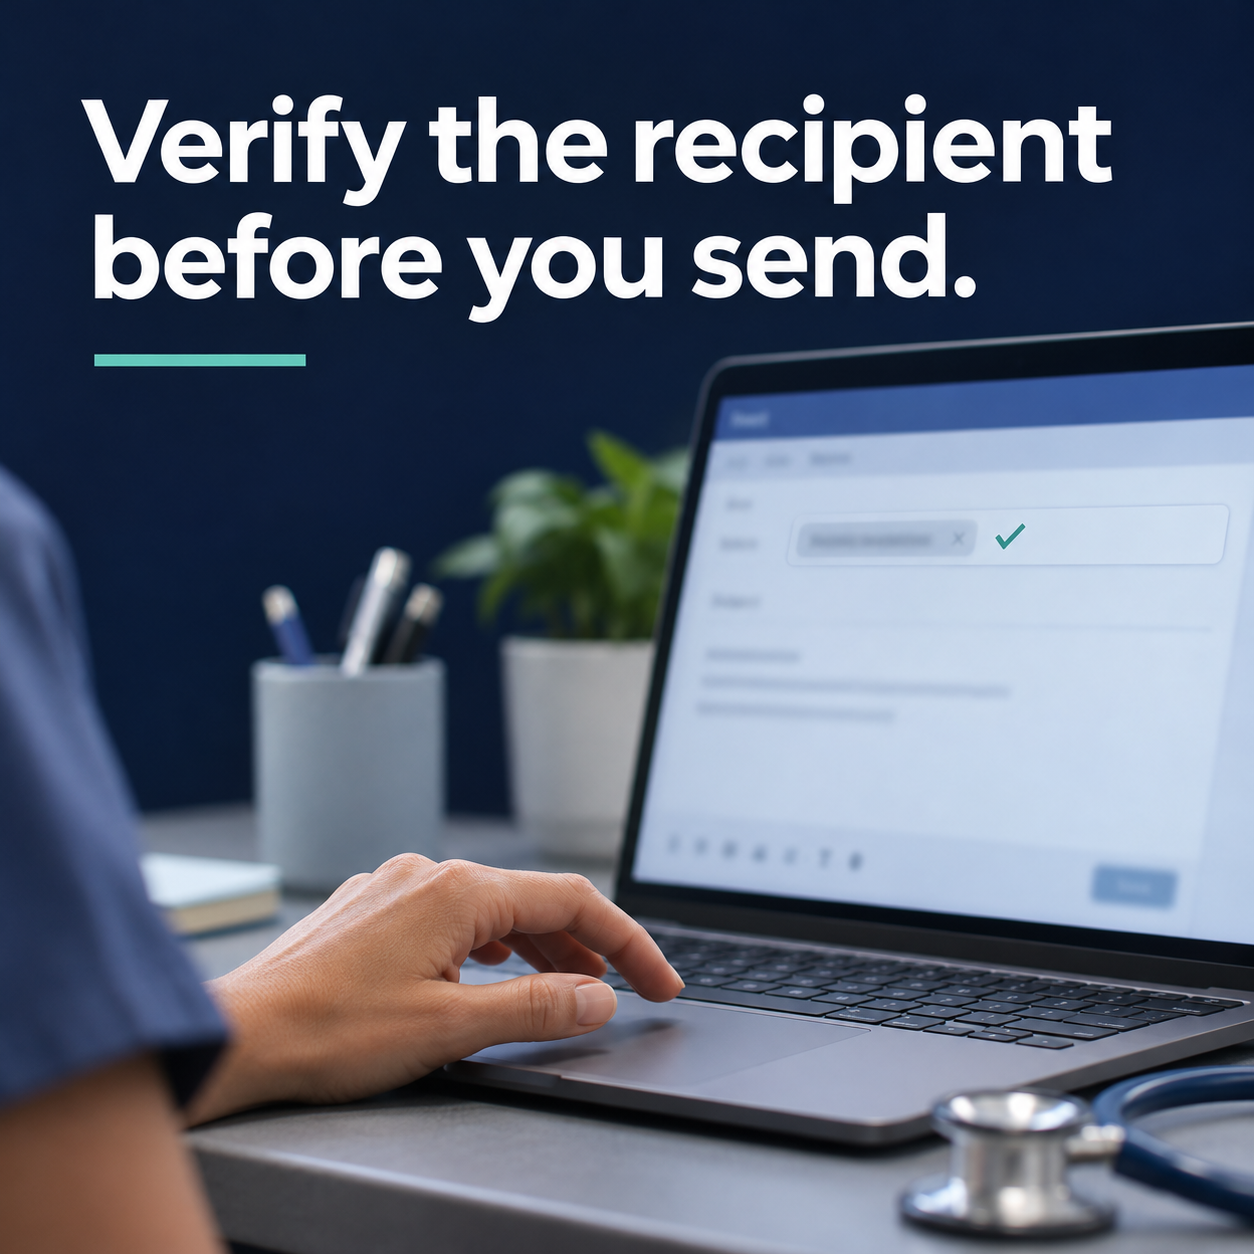
Verify the email address before sending PHI.
Confirm new addresses through a separate message or call.
Share only the information needed for the purpose.
Use secure portals for detailed records and sensitive attachments.
Honor reasonable requests for alternative confidential communications.
Train staff to pause before clicking “send.”
The best safeguard is often simple: verify the recipient first.