Who is responsible for updating every device connected to your network?
Most organizations assume their IT provider handles cybersecurity updates. However, that assumption can create serious security vulnerabilities.
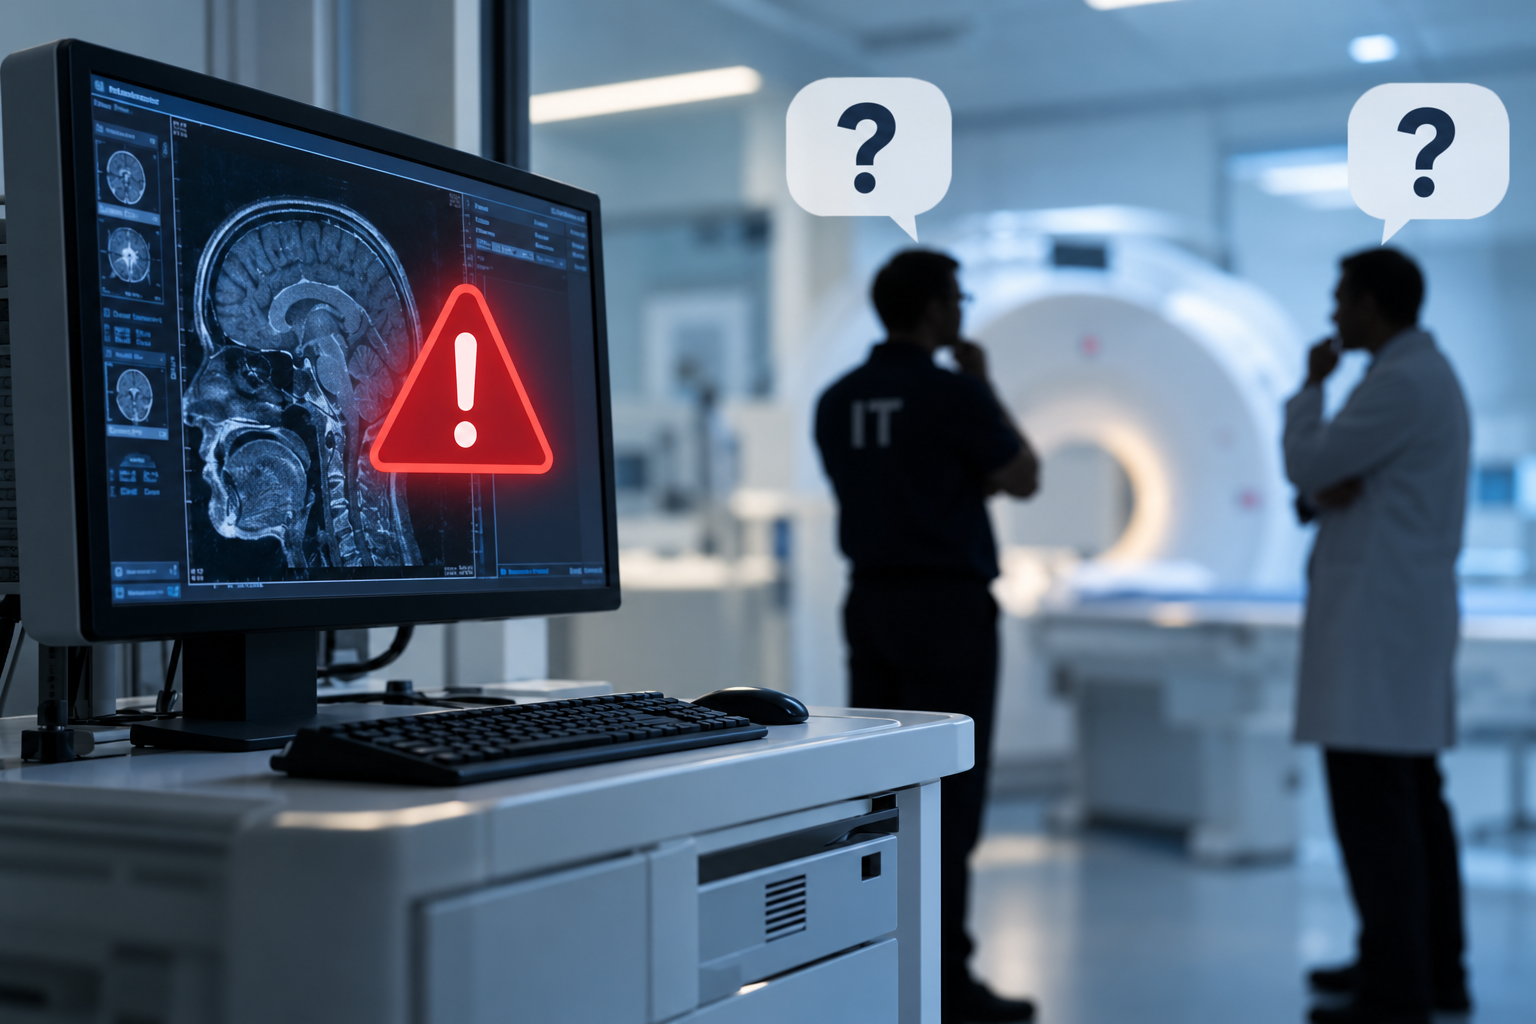
Consider this example… a specialty medical practice with an imaging workstation that had not received security updates in over a year. The workstation wasn’t hidden, and hackers hadn’t compromised it. It simply remained connected to the network without necessary security patches. The manufacturer had released a fix more than twelve months earlier. Yet nobody had installed it. Why? Because everyone assumed someone else was responsible.
When IT and Medical Equipment Vendors Assume Someone Else Is Responsible
The practice’s IT provider assumed the medical equipment vendor handled updates for imaging devices. Meanwhile, the equipment vendor assumed the IT provider managed security updates for network-connected systems. Neither organization intentionally ignored the vulnerability. Unfortunately, neither organization accepted responsibility for fixing it. The workstation remained vulnerable because nobody clearly defined who managed its security.
This situation highlights a common cybersecurity problem: Unclear responsibilities can leave your organization exposed to unnecessary risks. This example was a medical practice, however, business associates have the same responsibilities within their own network.
Medical Devices Can Create Hidden Cybersecurity Risks
Medical practices rely on more than desktop computers and electronic health record systems. Many medical devices connect directly to the practice’s network and may store, process, or transmit electronic Protected Health Information (ePHI).
These devices may include:
- Imaging workstations and diagnostic equipment
- Digital X-ray machines
- Ultrasound systems
- Laboratory analyzers
- Patient monitoring equipment
- Network-connected printers and scanners
- Medical equipment using embedded operating systems
Each connected device can introduce cybersecurity risks when organizations fail to maintain appropriate safeguards. Some medical devices also use outdated operating systems that manufacturers no longer support. Others require manufacturer approval before installing security patches. These restrictions make clearly assigned security responsibilities even more important.
HIPAA does not explicitly require every device to receive every available patch.
However, organizations must evaluate known vulnerabilities and determine appropriate security measures. A medical device containing ePHI cannot simply fall outside the practice’s security program because a vendor manages it. The practice must understand its risks and document appropriate protections.
Medical practices and business associates should take several important steps to identify and address vulnerabilities.
1. Maintain a Complete Asset Inventory
Identify every device connected to the network, including medical equipment, workstations, servers, printers, and wireless devices. Document operating systems, software, and vendors.
2. Assign Responsibility for Security Updates
Clearly identify who manages security updates for each device. Document whether the responsibility belongs to IT, the equipment manufacturer, another vendor, or the practice.
3. Review Vendor Agreements
Determine whether existing contracts address software updates, vulnerability management, security monitoring, and incident reporting. Never assume a vendor provides services that the agreement does not include.
4. Address Devices That Cannot Receive Updates
Some medical equipment cannot safely accept standard security patches. Organizations should evaluate compensating safeguards, including network segmentation, restricted access, and additional monitoring. Coordinate these protections with the manufacturer when necessary.
5. Document Findings and Corrective Actions
Record identified vulnerabilities, assigned responsibilities, planned safeguards, and remediation progress. Include unresolved risks in the practice’s Risk Management Plan. Review these records regularly and whenever significant changes occur.
The Real Problem Isn’t the Missing Patch
A missing patch creates vulnerability. However, unclear responsibilities can allow vulnerabilities to remain unresolved. Neither the IT provider nor the equipment vendor deliberately neglects the device. Both assumed someone else handled it. This simple misunderstanding can expose patient information and disrupt essential medical services.
Every device needs an owner, and every security responsibility needs clear documentation.
Ask your IT provider one important question:
“Who handles security updates for every device on our network, including medical equipment?”
Then ask your vendors the same question.
If their answers differ, your practice may have an important security gap.
Identifying these gaps now can help prevent costly security incidents later.
When was the last time your organization updated the asset list?
At Aris Medical Solutions, our HIPAA Keeper™ cloud-based platform makes HIPAA compliance simple. It guides your organization through every requirement with a clear, step-by-step process. From risk analyses, risk management, policies to employee training, and required documentation, you’ll have everything needed to remain compliant, protected, and audit-ready. Best of all, your HIPAA Compliance Officer is never on their own. Every client has access to a Certified HIPAA Security Analyst who provides expert guidance, answers questions, and helps ensure your compliance program is implemented correctly.
Schedule your HIPAA compliance review today and protect your organization from the next enforcement headline.
Your Trusted Partner for HIPAA Compliance since 2009